Cybersecurity & AI.
Simplified.
Pro CISO® brings CISO-level expertise directly to your organization, in the form of a service. By blending together experts, solutions and guidance, we make enterprise-grade cybersecurity pragmatic, measurable and continuously improving - without the complexity. Attackers already operate at AI speed, so we do too: on platforms we build and operate ourselves - CA/CR® ReconX and ProDesk, at the heart of our SOC Service - and in the applications our customers own outright.
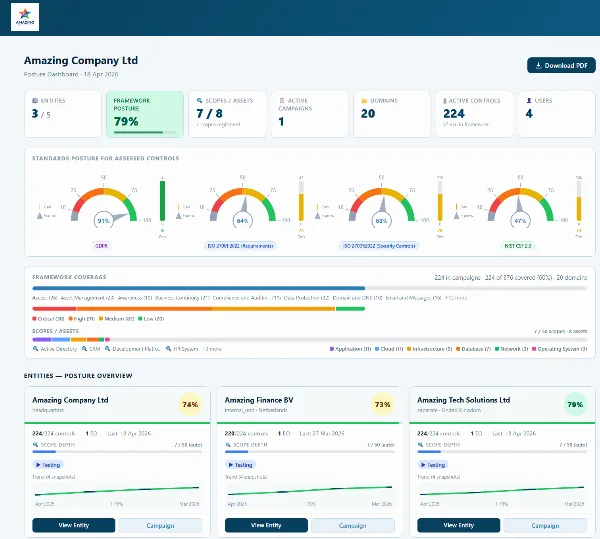
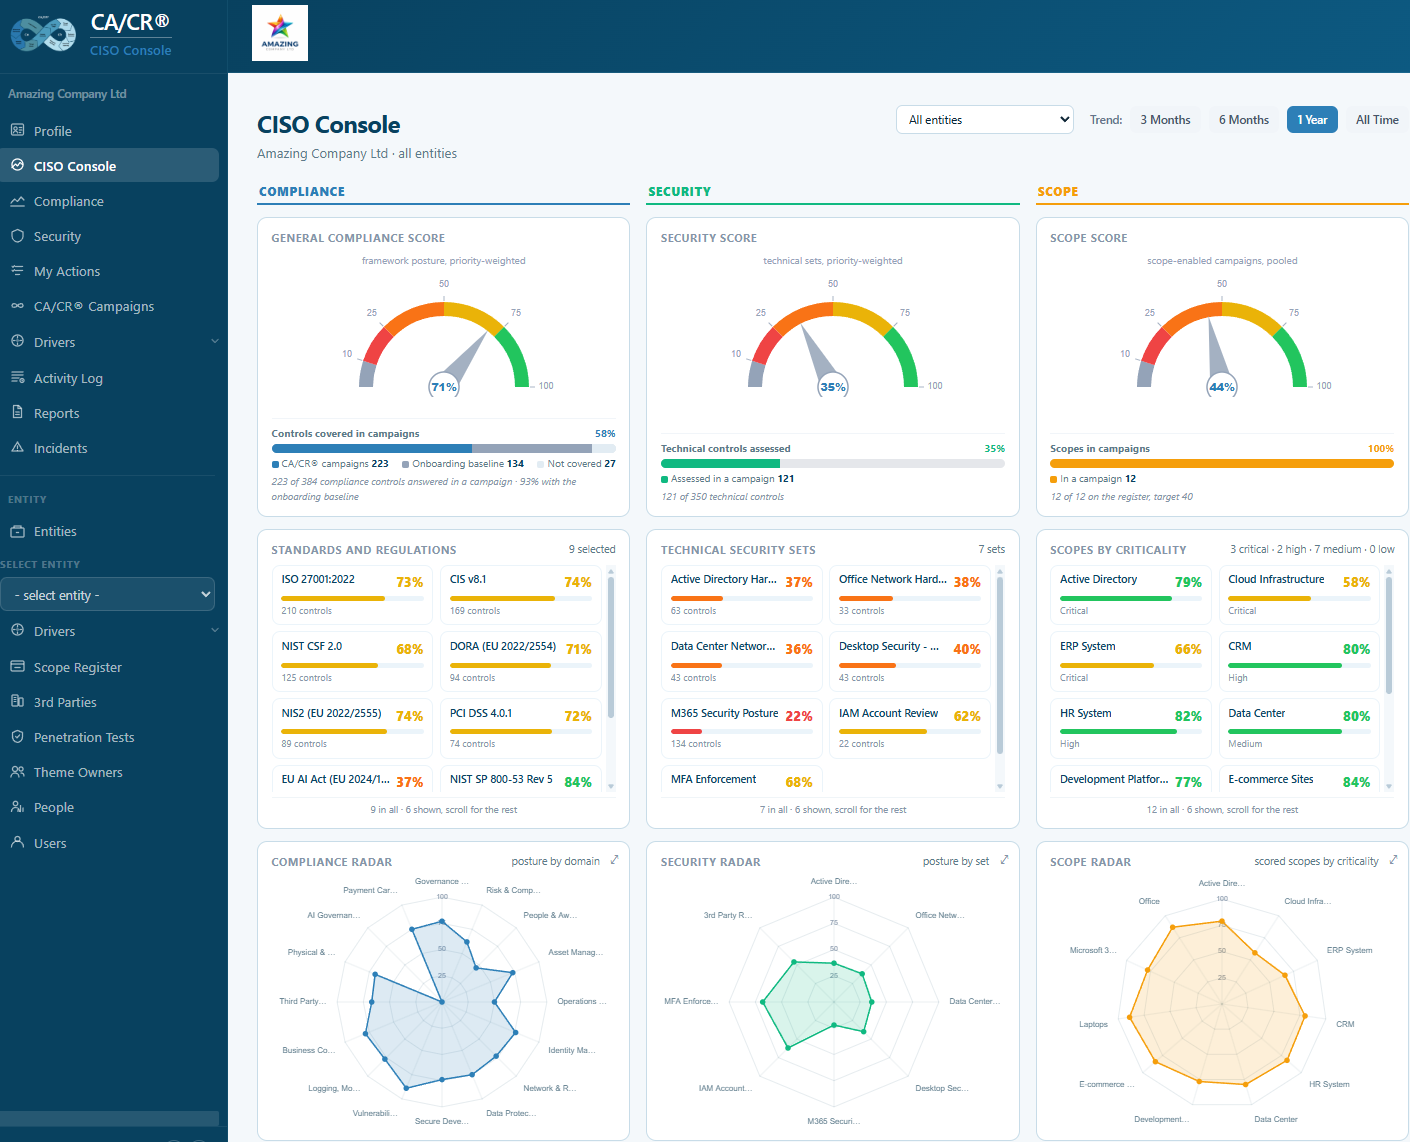
Advisory expertise and a purpose-built CA/CR® CISO Console platform, working as one - transforming cybersecurity from a compliance exercise into a continuously measured and improving security enhancement practice.


Managed Services
Our experts run your security programme with you - from a dedicated CISO to round-the-clock monitoring, assessments and testing.
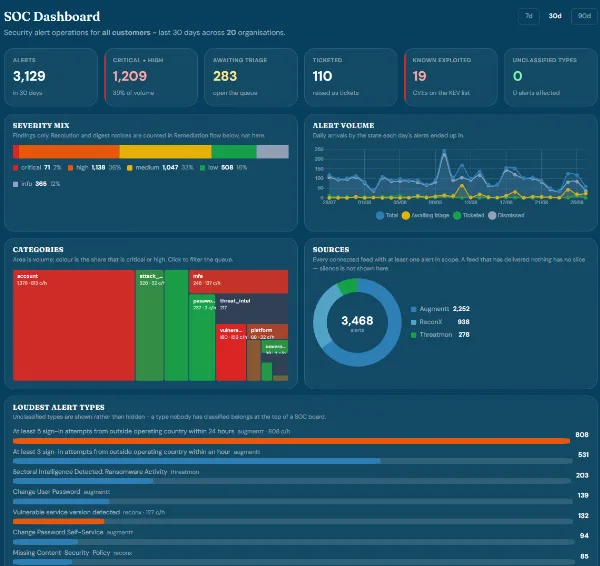
Managed SOC
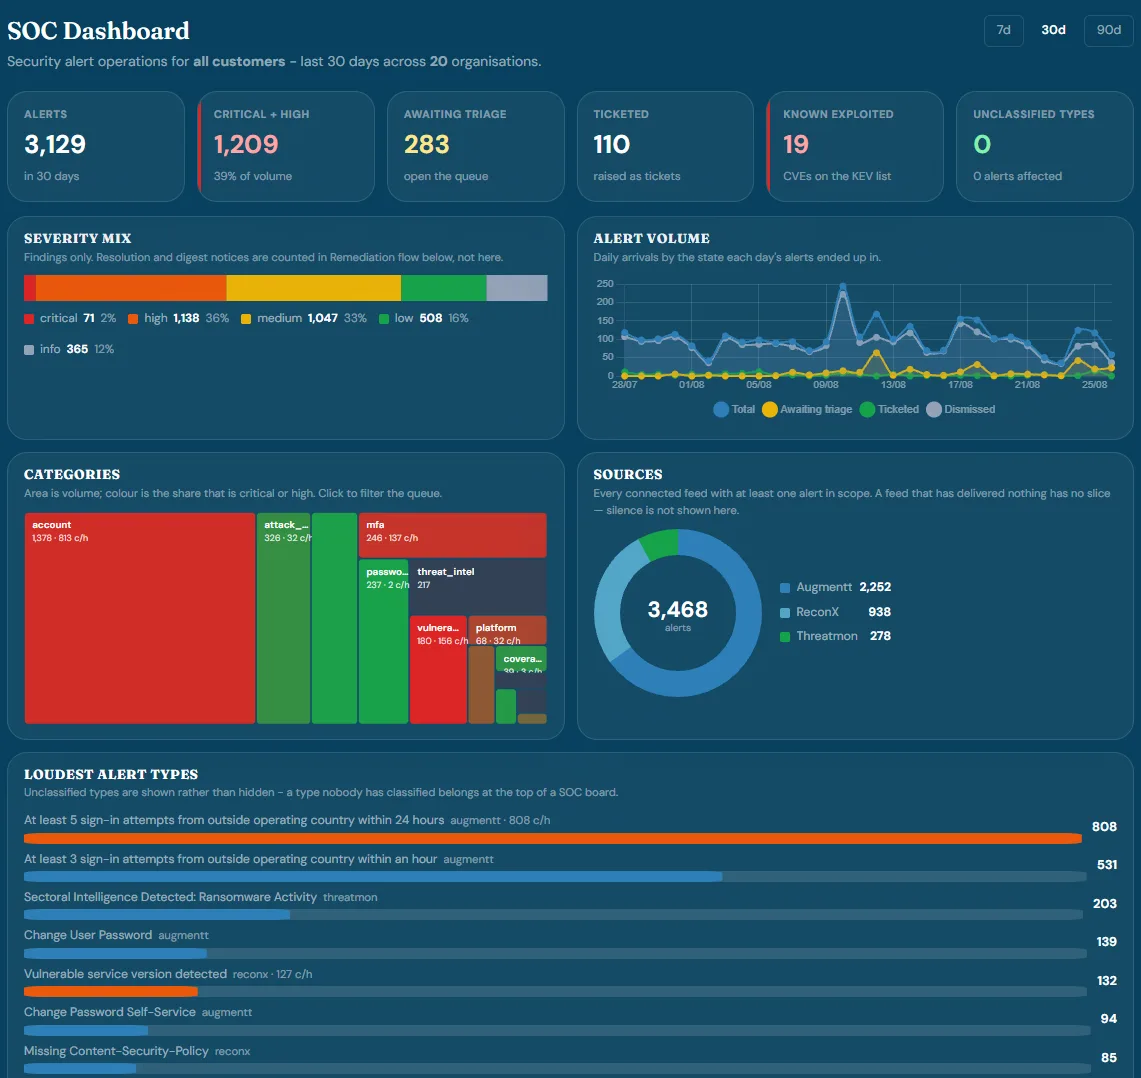
Activate a fully managed SOC in 24h ! Address 80% of the risks by monitoring user accounts and exposed vulnerabilities. Monitor M365 alerts, ReconX attack surface exposure
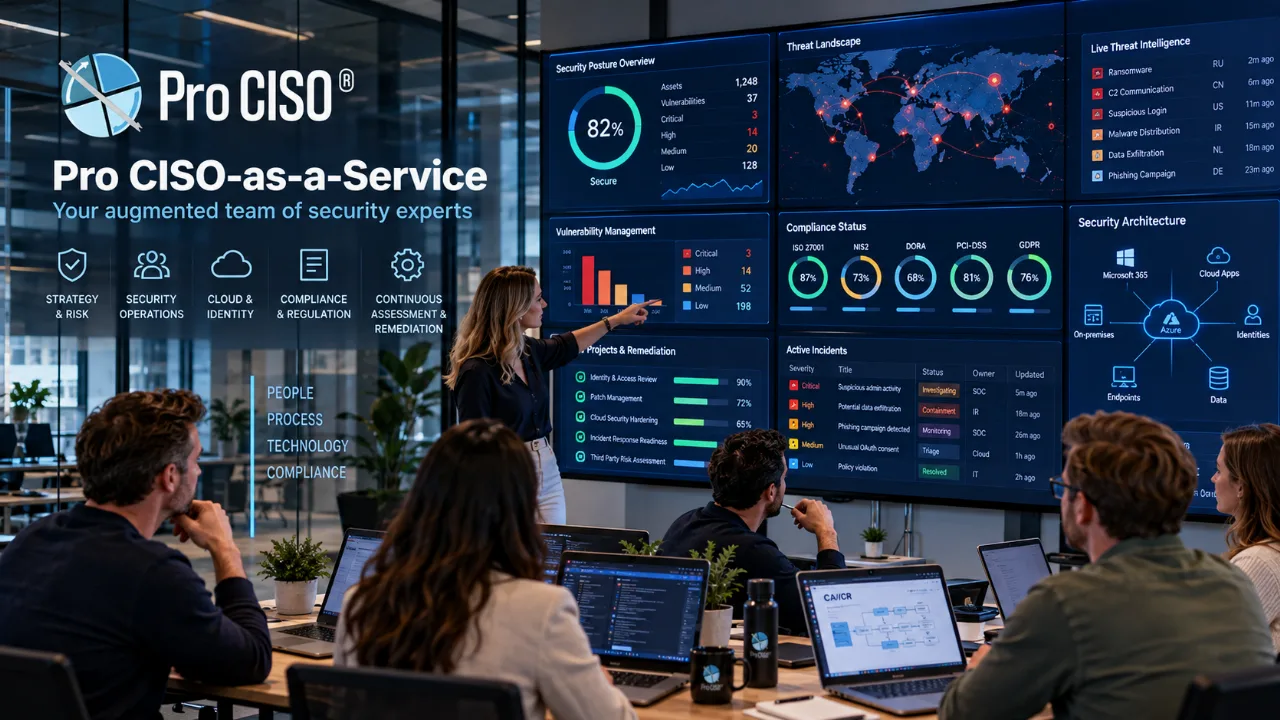
Pro CISO-as-a-Service
An assigned CISO, augmented by a pool of experts specialised in their vertical field. Enterprise-grade security leadership - without the full-time hire.
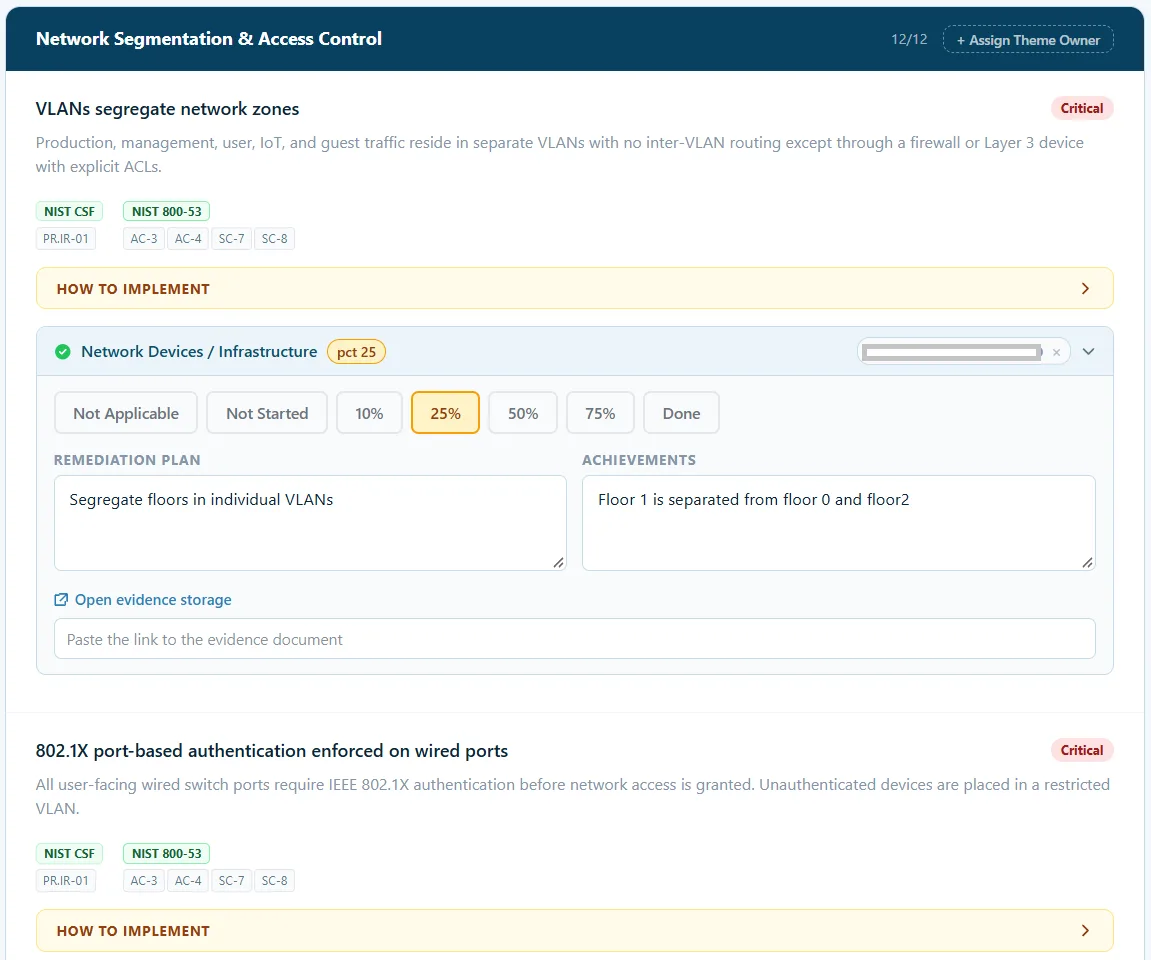
Security Assessments
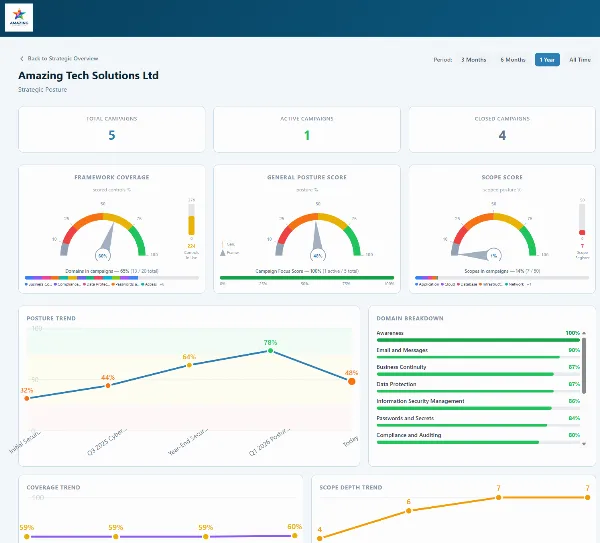
Know exactly where you stand - a structured evaluation giving a clear, visual picture of your security posture and compliance readiness.
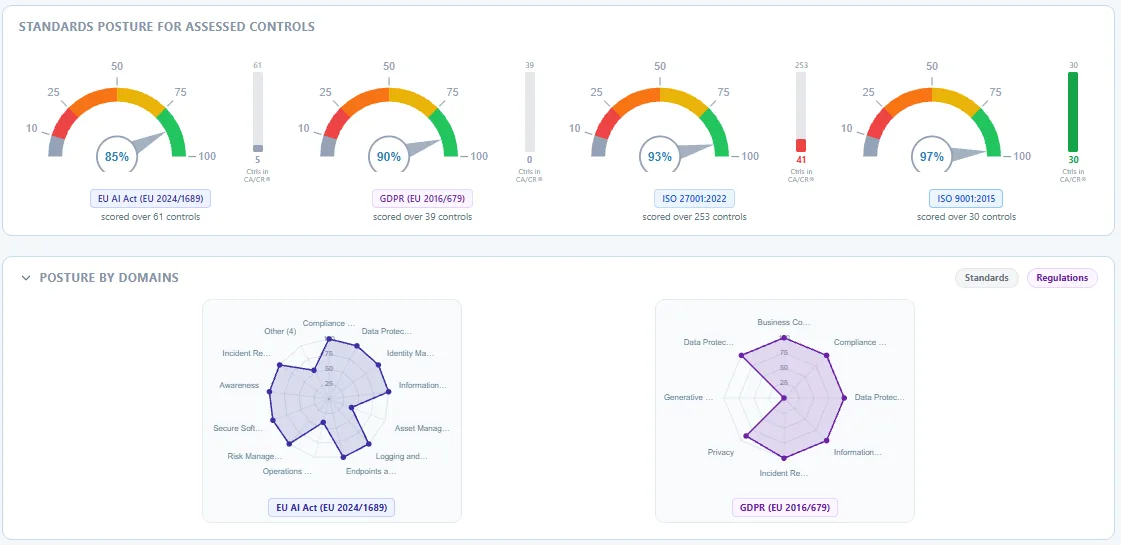
EU Regulations Assessments
A fixed-price, fully online assessment of your readiness against GDPR, NIS2, DORA and the EU AI Act.
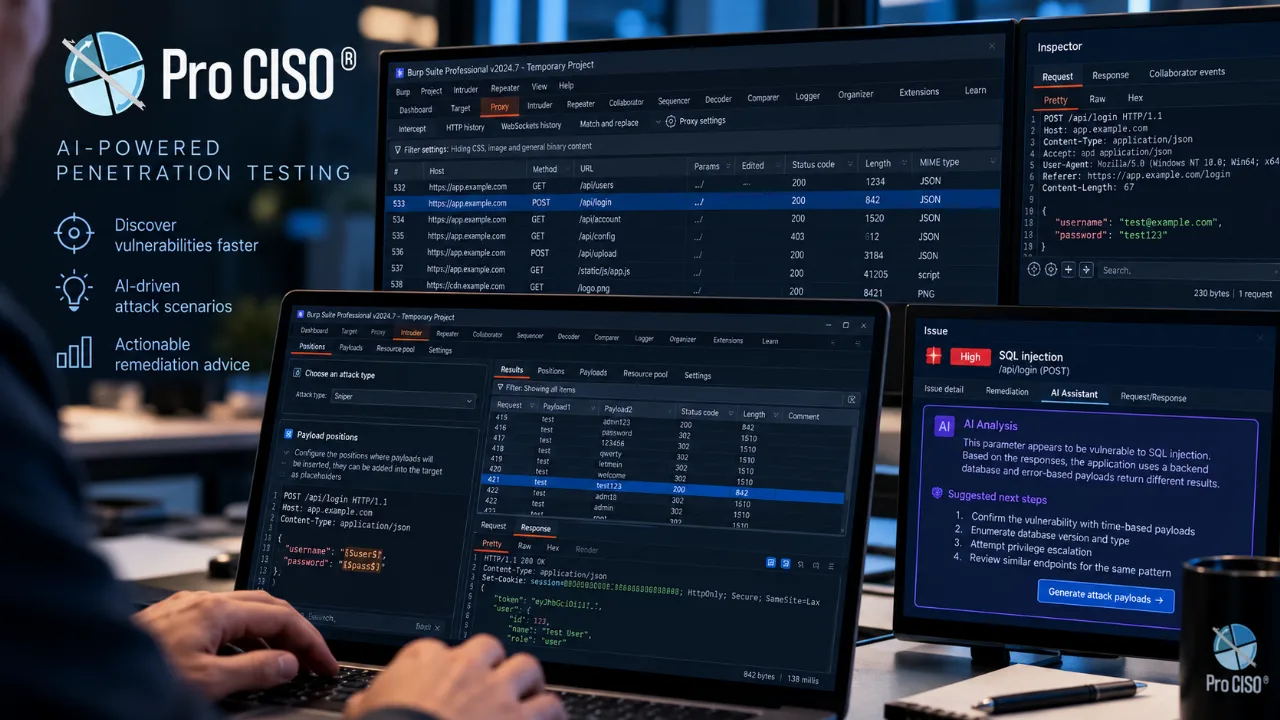
Pentest Fusion
Integrated threat modelling and penetration testing, built for software development teams and enterprise environments.

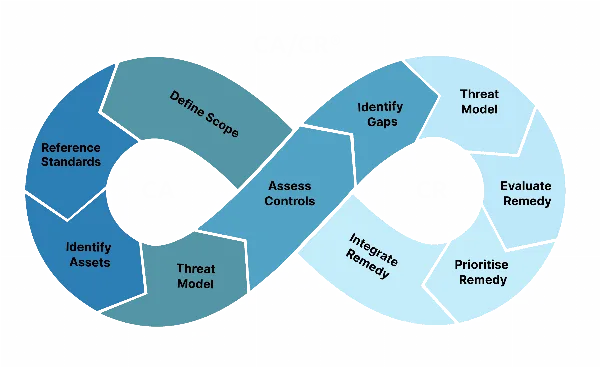
CA/CR® - Continuous Assessment / Continuous Remediation
Our proprietary approach mimics DevOps: start small, iterate fast, expand progressively. Assessments can begin on limited scopes and grow in both width (control frameworks) and depth (assets and legal entities).
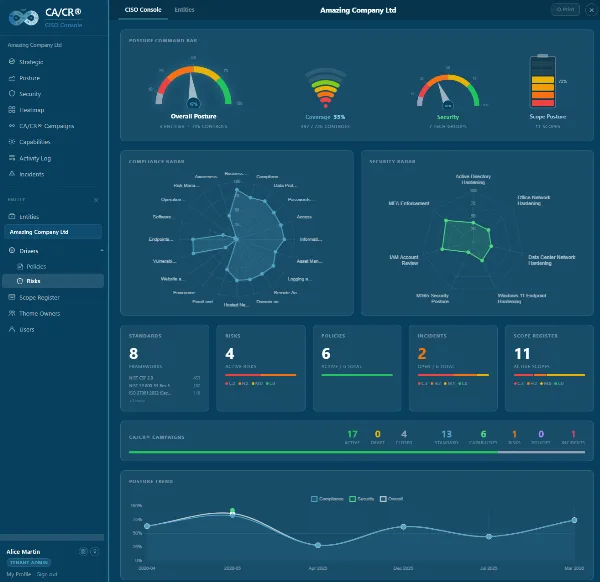
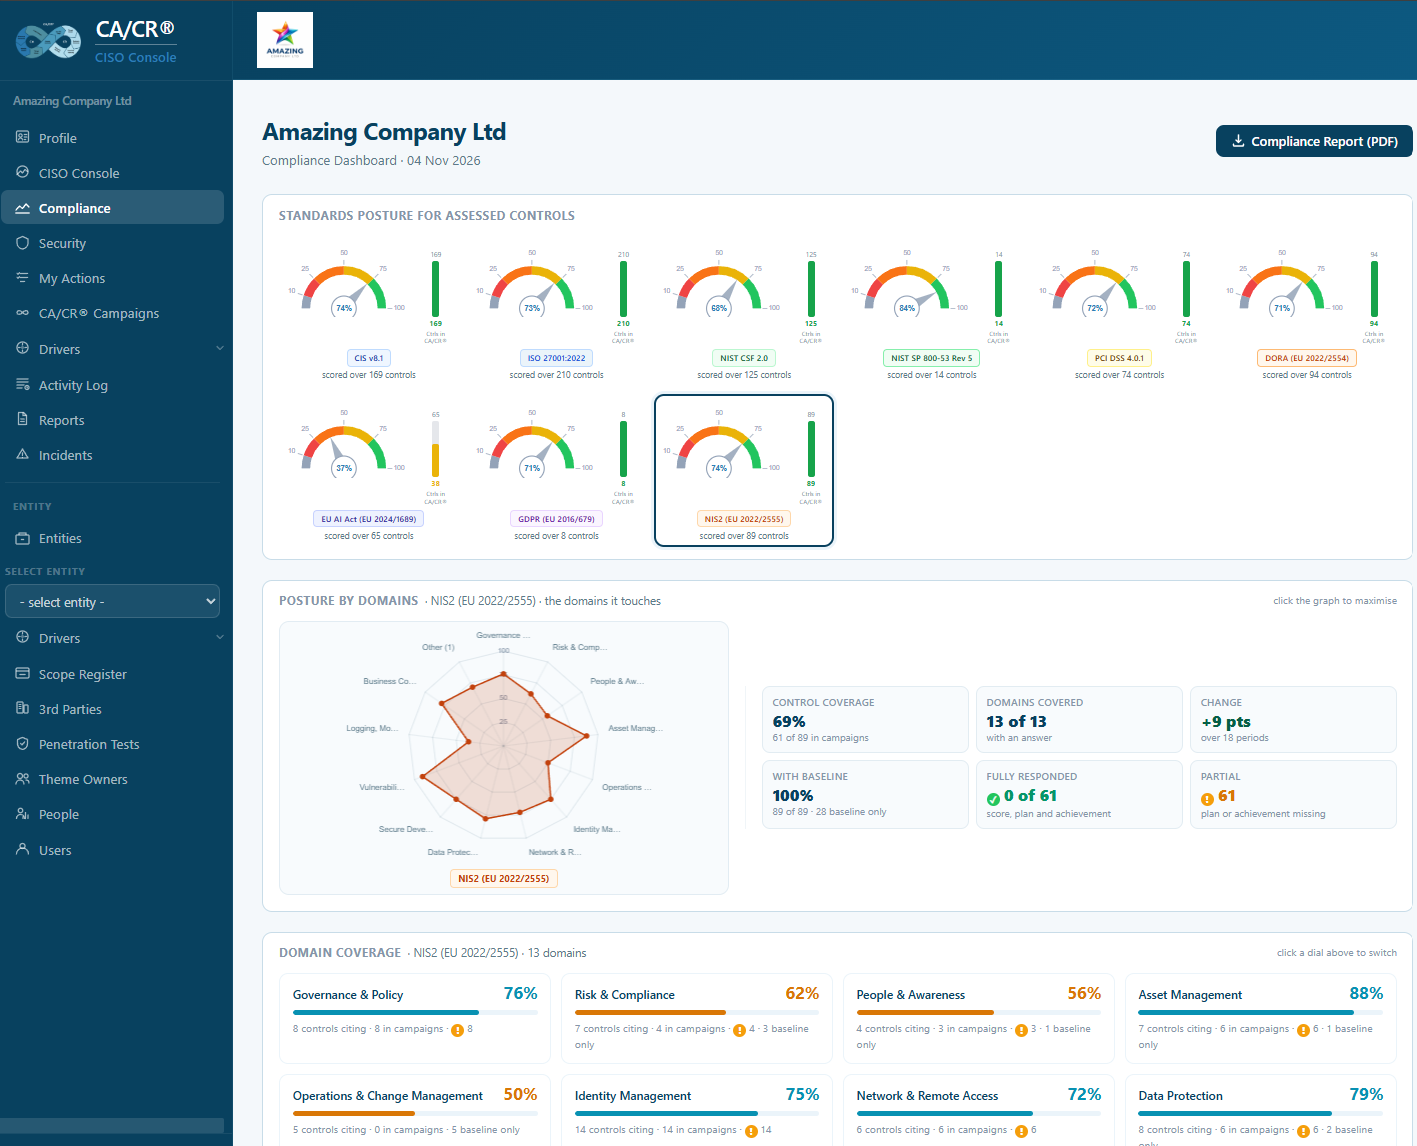
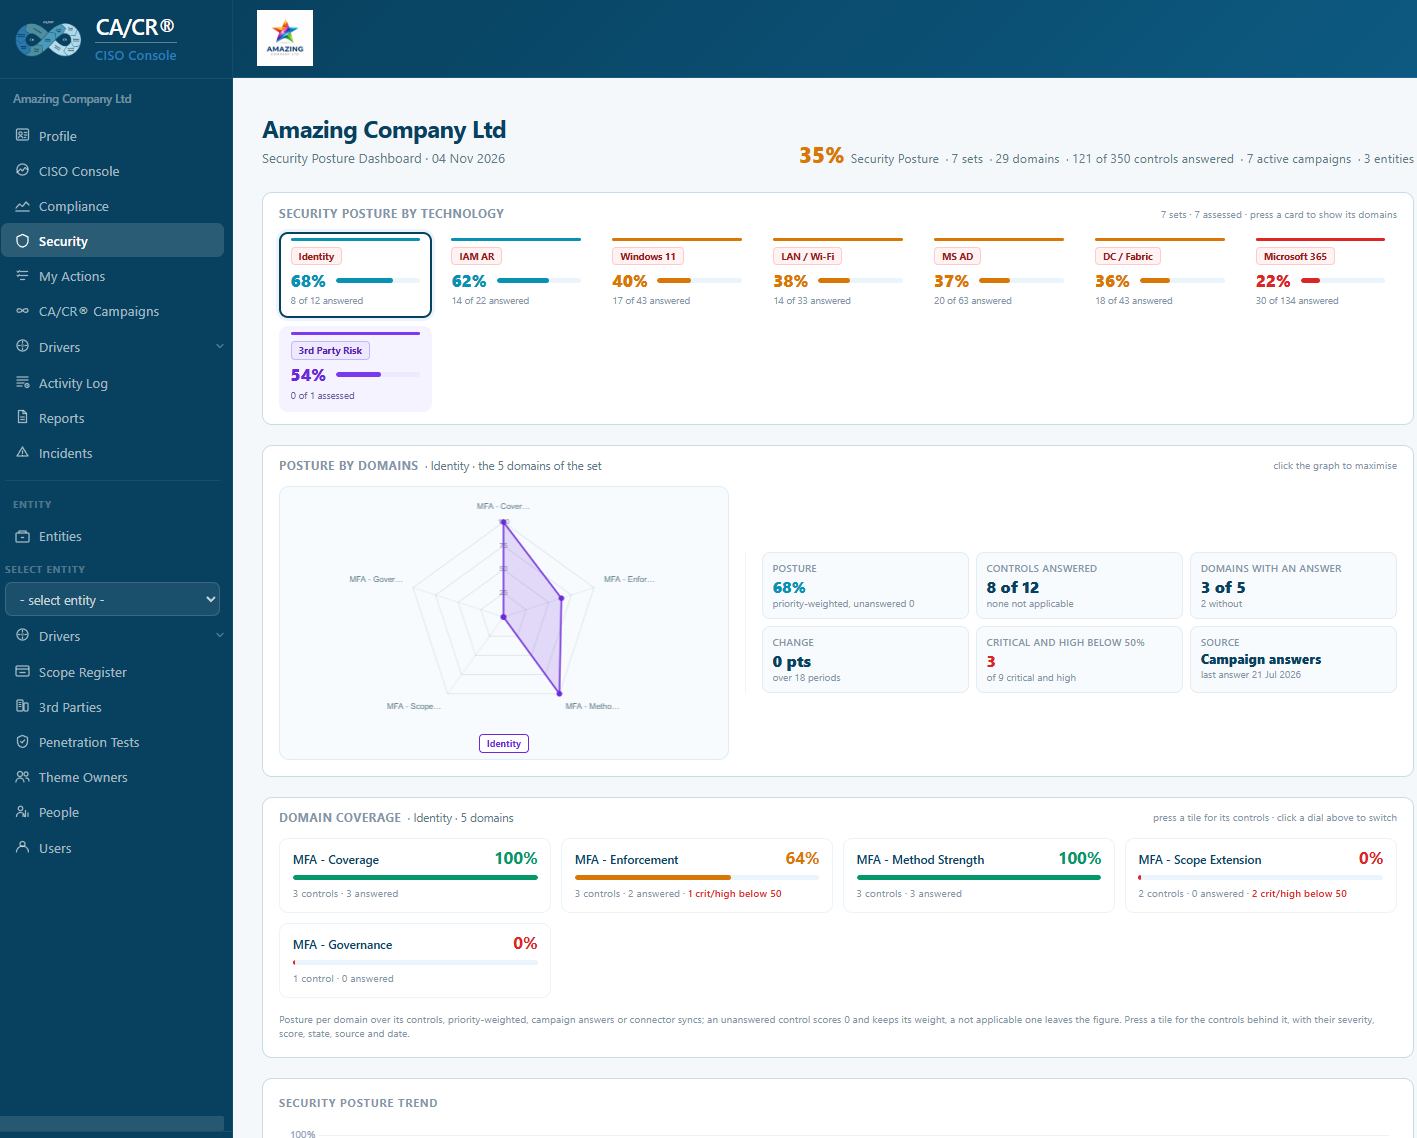
CA/CR® CISO Console - Pragmatic Security Posture Management
Our innovative SaaS platform lets companies rapidly assess security posture across all legal entities. Simple, pragmatic, and powered by the CA/CR® methodology.
Resources & Publications
Articles, practical guides, service briefs and thought leadership from our CISO team.
 Methodology · Latest
Introducing the Pro CISO® Sales Partners Program
A new opportunity for freelancers, consultants, agencies and businesses to generate revenue by promoting innovative cybersecurity solutions -supported by a certified cybersecurity company, proprietary technology and a dedicated Sales Partners Portal. Mario Procopio, Pro CISO · 9 November 2026 · 6 minute read
Pro CISO® is more than just a brand, it's a statement.
What's in a name?
"Pro" comes from Latin, meaning "in support of" or "in assistance to", reflecting our commitment to empowering CISOs and organisations with expert guidance. It also stands for "Professional CISO", providing top-tier cybersecurity leadership to companies that lack a dedicated CISO but require strategic security expertise.
Founded in Amsterdam, 2020
Pro CISO® is a cybersecurity company with a clear mission: remove the challenges of attracting cybersecurity talent, or dealing with hefty consultants, by providing flexible security teams at your service. With Pro CISO® you receive a front-facing CISO or CISO wingman, with an augmented team of security experts, each specialised in their own domain. As priorities shift in our dynamic industry, it is crucial to have the flexibility of deploying different expertise depending on the need. Pro CISO®-as-a-Service does just that - your extended team with all-round expertise that never fails to deliver.
Our commitment
At Pro CISO®, we are committed to providing exceptional, highly productive professionals. By staying lean, focused, and humble, we ensure that our clients receive the right expertise and hands-on execution without the inefficiencies of a bloated workforce.
Let's simplify your cybersecurity
Whether you need a fractional CISO, a managed SOC, a penetration test, help building and governing your own applications with AI, or want to see CA/CR® in action - we're here.