News
cybersecurity Microsoft Disrupts Chinese-Language Phishing Market Behind 1B+ Messages - SecurityWeek cybersecurity CISA warns admins to immediately fix Ivanti flaw exploited as zero-day - BleepingComputer cybersecurity Anthropic warns small AI models could self-replicate through IoT devices - Ars Technica Security vulnerability VU#166125: Bisheng has authentication bypass vulnerabilities - CERT/CC Vulnerability Notes cybersecurity CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts - The Hacker News ai Anthropic Research Warns of Self-Replicating AI Threat to IoT Devices - IoT Business News - Anthropic - Claude AI cybersecurity Windows Server Zero-Day Flaw Lets Attackers Crash Systems With a Single Malicious Packet - CyberPress threat-intel Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution - GBHackers cybersecurity curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution - The Hacker News ai The Download: faking blood and the future of batteries - MIT Technology Review threat-intel Meta GitHub Repositories Compromised, Exposing Software Code and Employee Personal Data - GBHackers cybersecurity Hirudo Android malware replaces banking apps to evade security checks - BleepingComputer cybersecurity Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution - CyberPress cybersecurity Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days - The Hacker News cybersecurity Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks - The Hacker News
1 / 15
All news ›
← Back to the Toolkit

Bitdefender XDR

The best alternative to Microsoft Defender, for achieving defense in depth and avoiding using the same vendor for both office and anti-malware solutions. Once central console to manage all endpoint policies and alerts.

Built for Enterprises and SMEs
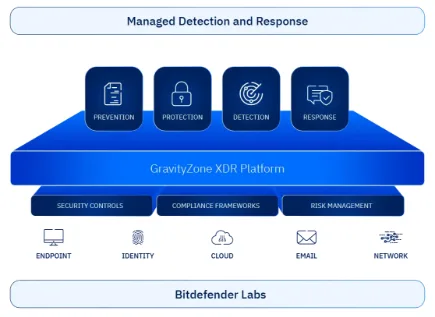
Bitdefender XDR

About Bitdefender XDR

Centralized visibility across multiple security layers.

Earlier threat detection by correlating events from different sources.

Reduced alert noise through automated correlation and prioritization.

Faster incident response with contextual threat information.

Identity and cloud monitoring beyond traditional endpoint security.

Single investigation view for security incidents and attack paths.

What you get

  • Provides centralized detection and response by correlating security signals across endpoints, identities, cloud services, networks, and applications. It identifies suspicious activity across the environment and provides greater context for investigating and responding to threats.

Interested in Bitdefender XDR?

Tell us what you need - tick it in the contact form and our team will come back to you.

Contact us