← Back to the Toolkit
Our Platforms
CA/CR CISO Console
Empower the CISO (corporate or consulting) with a platform to manage Policies, Risks, Incidents, Asset Register, 3rd Parties, and run Security Assessment campaigns for all of these modules.
Built for Enterprises, SMEs and consulting CISOs
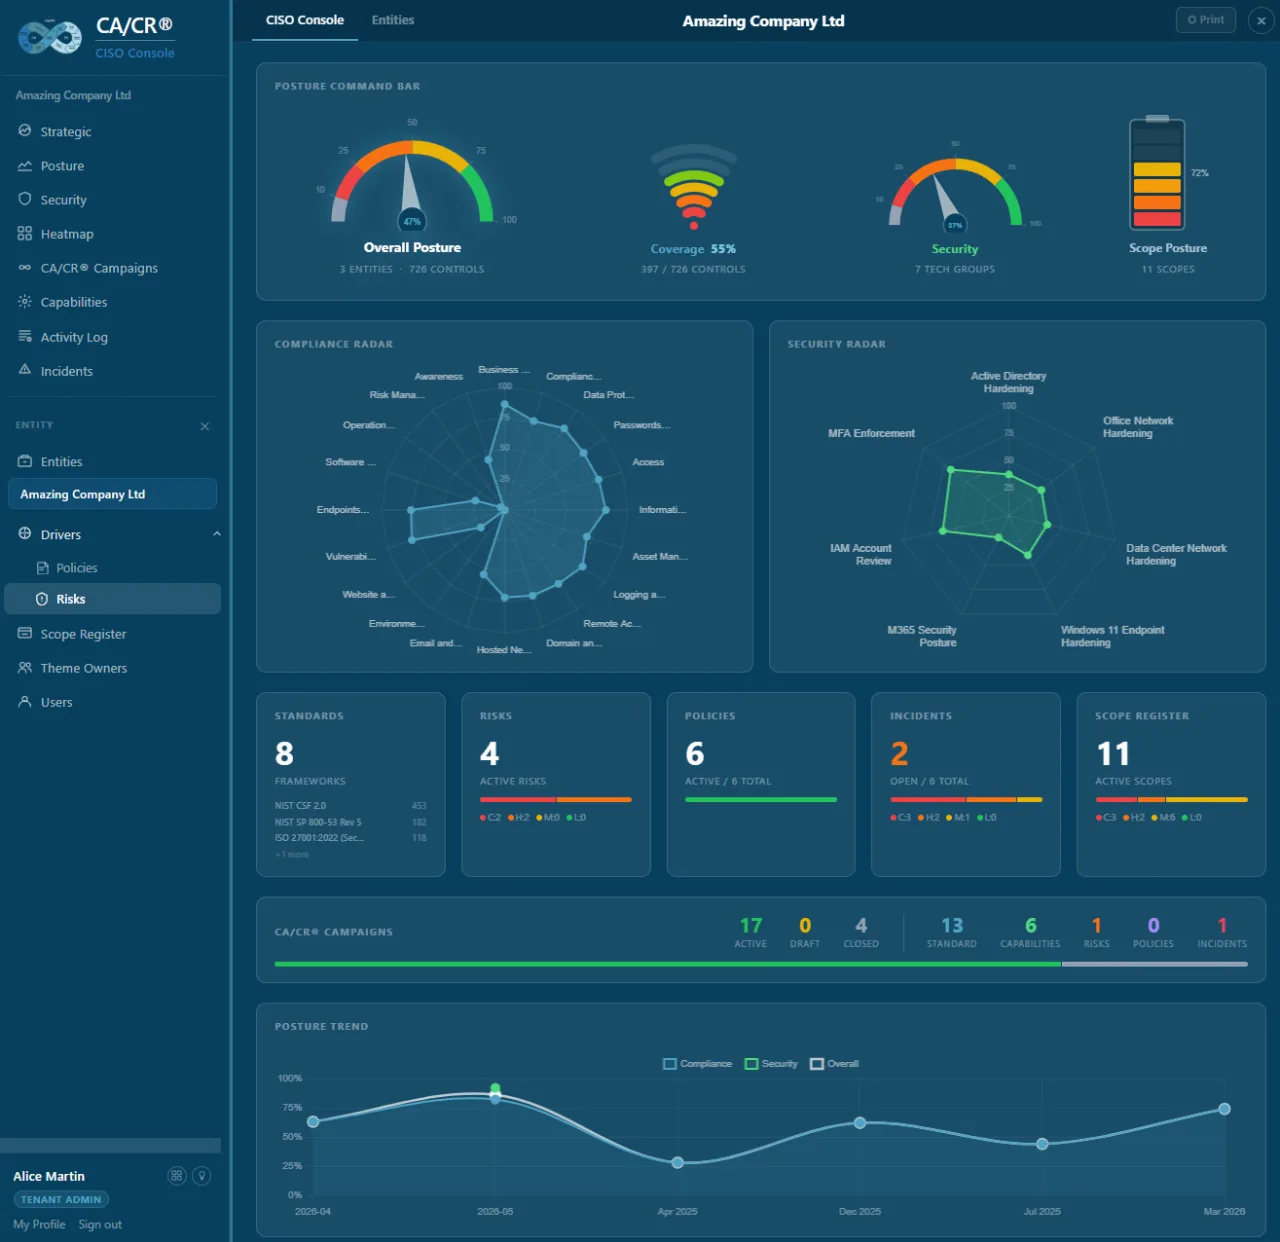
About CA/CR CISO Console
What you get
- Standards Framework - ISO 27001, NIST CSF, PCI-DSS, CIS & more, mapped once
- Regulations Framework - NIS2, DORA, GDPR & AI Act coverage built in
- CA/CR® Campaign Engine - dispatch assessment sprints in a click
- Scope Register - define crown-jewel assets and boundaries
- Theme Owners - delegate questionnaires to the right experts
- Reports - version-controlled, audit-ready PDF reports
- Incidents - track incidents with GDPR / NIS2 / DORA / AI Act flags
- 5 Entities - assess up to five legal entities
- Unlimited platform users - add your whole team, no seat limits
- Unlimited external Theme Owners - invite unlimited external contributors
- 3rd Parties (20) - assess up to 20 vendors in a separate risk lane
- Policies - 40+ templates, tailored and exported as polished PDF
- Risks - likelihood × impact register, tied to remediation
Interested in CA/CR CISO Console?
Tell us what you need - tick it in the contact form and our team will come back to you.
Contact us