ISO 9001/27001 IMS
ISO 9001/27001 certification simplified with the IMS functions within CA/CR® CISO Console
Built for Enterprises, SMEs and consulting CISOs
About ISO 9001/27001 IMS
Introducing the Integrated Management System in CA/CR® CISO Console
Most organisations run their management system in two places: the work happens in tools, and the proof lives in documents that someone has to keep in step by hand. Before every audit the scramble is the same. Which version of the manual is current? Does the risk count in the Management Review match the register? Who owns this procedure?
The new IMS capability in CA/CR® CISO Console closes that gap. It brings the foundations of your management system and the documents that describe it into the same platform that already holds your risks, policies, controls and assessments.
Start from your foundations. Record the scope of the management system, the context of the organisation, interested parties and their expectations, the yearly SWOT analysis, objectives with measures and owners, roles and committee, the Statement of Applicability, and internal audits with their findings. Each is entered once and reused everywhere.
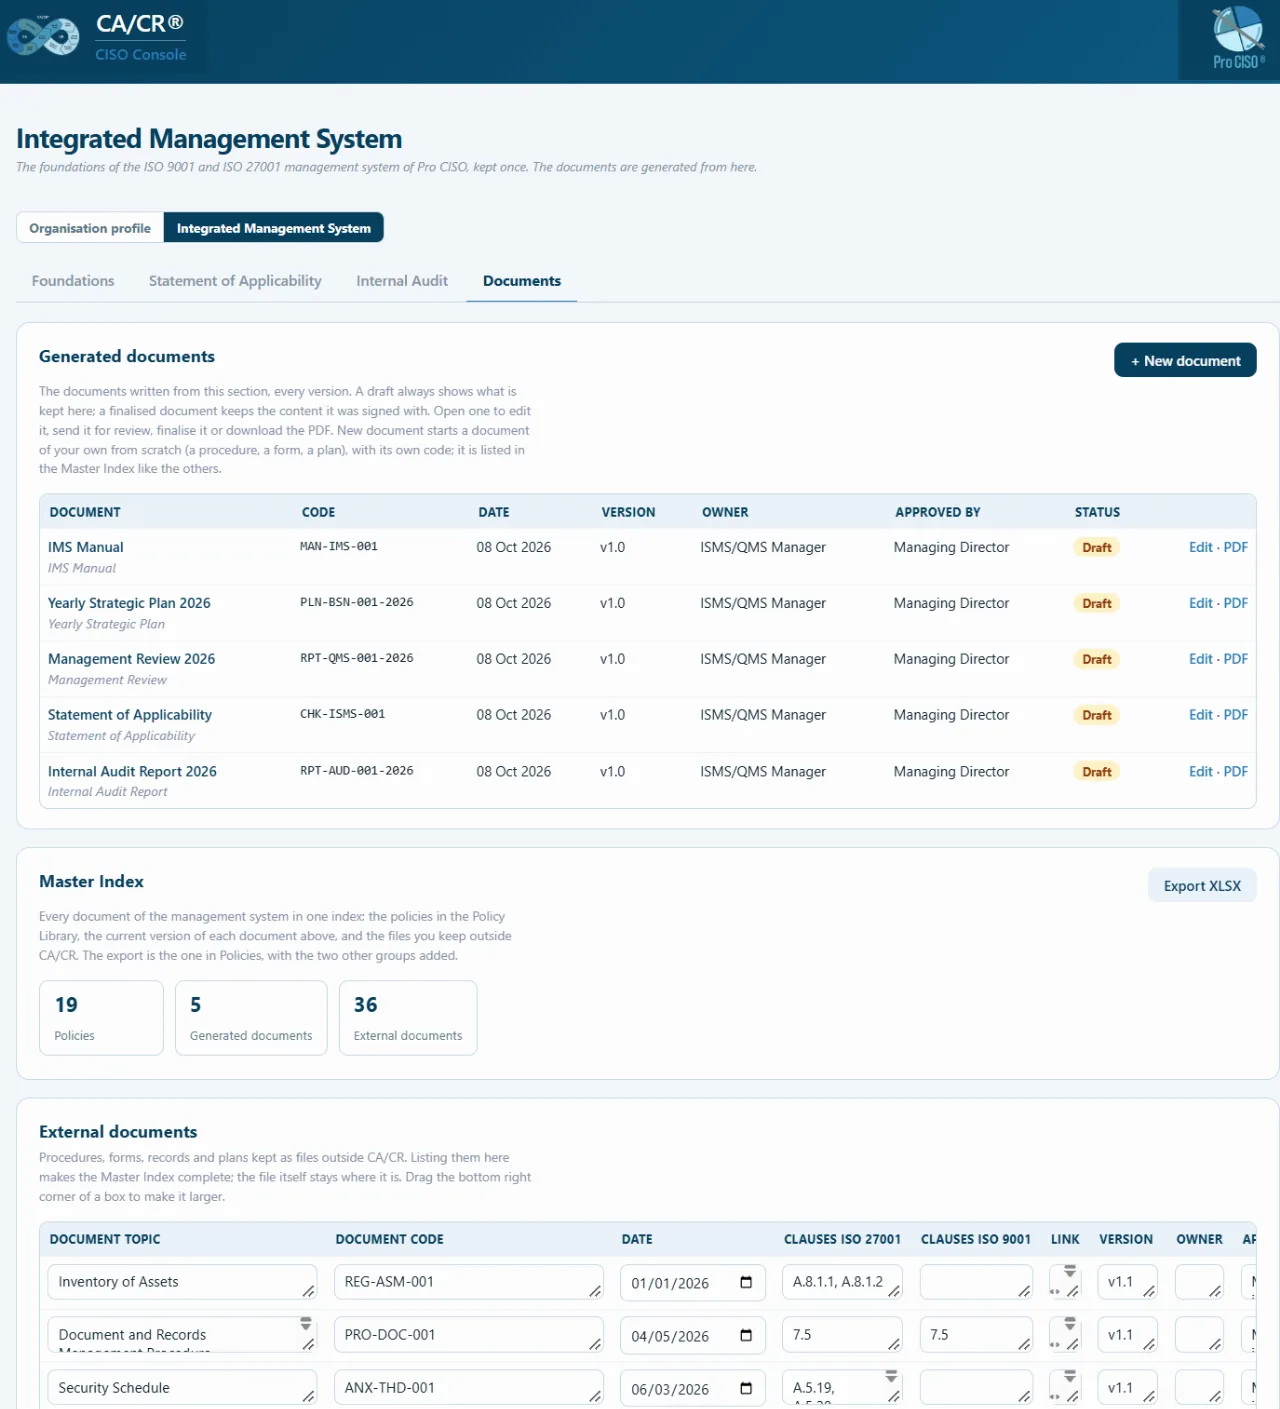
Generate the documents auditors ask for. With one click the platform produces the IMS Manual, the Yearly Strategic Plan, the Management Review, the Statement of Applicability and the Internal Audit Report. Each is structured along the clauses of ISO/IEC 27001:2022 and ISO 9001:2015 and filled with your own content and live figures. Need a procedure, a form or a plan of your own? Create it from scratch with the same editor and your own document code.
Living drafts, immutable records. While a document is a draft, it stays current: add a risk, close a finding or improve your posture, and the document follows. When it is approved it is locked with the figures of that day, versioned, and available as a branded PDF. The next version starts from the last one.
One index for everything. The Master Index brings together your policies, the generated documents, your own documents and external references, each with its code, version, dates and owner. It is the list an auditor asks for first, and it can be exported.
Built for integrated certification. Information security and quality are managed as one system, not two. Organisations that hold or pursue ISO/IEC 27001 and ISO 9001 maintain a single manual, a single review and a single set of objectives.
The Integrated Management System is available now in CA/CR® CISO Console and is activated per organisation on request.
CA/CR® CISO Console by Pro CISO®: your management system, kept current and ready to show.
What you get
- One management system instead of a folder of documents. Scope, context, interested parties, SWOT, objectives, Statement of Applicability, internal audits and findings are kept in one place and maintained once.
- Audit-ready documents in minutes. The IMS Manual, Yearly Strategic Plan, Management Review, Statement of Applicability and Internal Audit Report are generated from your own data.
- ISO/IEC 27001 and ISO 9001 together. One integrated system covers both standards, including the 2024 climate change amendments, so nothing is written twice.
- Figures that are never out of date. Risks, posture, incidents, suppliers and audit findings in a draft follow the live platform. Once approved, the document is frozen as the signed record.
- Your wording, kept. Edit any section in your own words and the platform leaves it alone.
- A complete Master Index. Policies, generated documents, your own procedures and forms, and external documents are listed with code, version, dates and owner, and can be exported.
- Evidence behind every statement. The documents draw on the same risk register, policies, CA/CR® Campaigns and controls your teams already work with.
- Less consultancy time on paperwork. Time goes to improving security and quality instead of formatting and reconciling documents.
Interested in ISO 9001/27001 IMS?
Tell us what you need - tick it in the contact form and our team will come back to you.
Contact us