ReconX Attack Surface Management
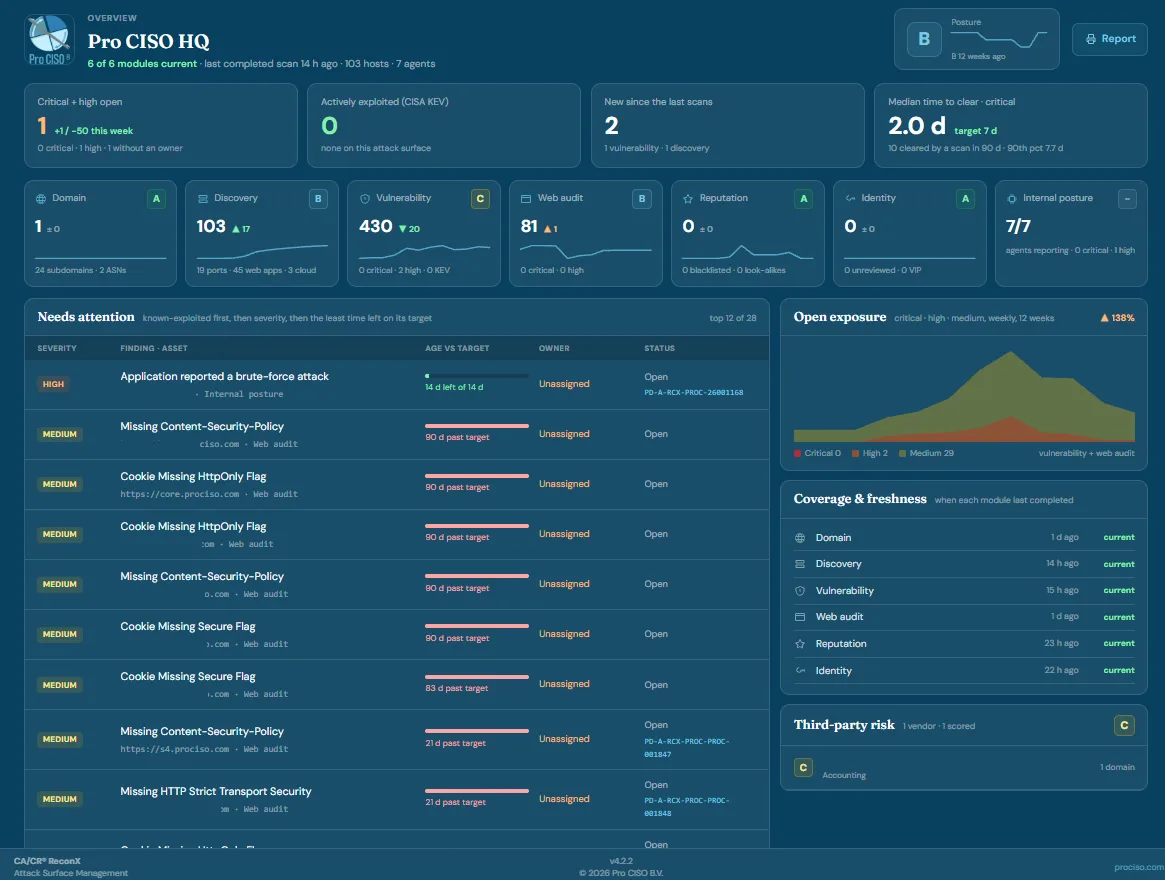
We only need the customer's domains to scan their public facing attack surface. -Domain Mapping, -Host Discovery, -Vulnerability, -Web Audit, -Reputation, -3rd-Party Risk, -Credentials on the Darkweb, -Internal Posture (Linux)
Built for Enterprises
About ReconX Attack Surface Management
Pro ReconX: your attack surface, seen the way an attacker sees it
Activating Pro ReconX takes one piece of information: your domain name. You do not need to supply IP ranges, asset spreadsheets or network diagrams, and nothing has to be installed.
From the domain alone, ReconX maps what your organisation exposes to the internet, including the systems nobody remembered to list.
Coverage then stays current by itself: new subdomains, servers and services are picked up as they appear, and retired ones drop out.
What you get
- A complete, living inventory. Every domain, subdomain, host, open service and web application you expose, with what changed since last time.
- Vulnerabilities ranked by real risk. Findings are prioritised by how likely they are to be exploited, not just by a severity score, so your team knows what to fix first.
- Website security checks. Encryption, certificates, security headers and configuration weaknesses across every site, with early warning before a certificate expires.
- Brand and e-mail protection. Look-alike domains that could be used for phishing, blocklist monitoring, and the health of your e-mail authentication.
- Leaked credential monitoring. Alerts when company accounts appear in breaches or stolen-password collections.
- Supplier risk. A security scorecard for the third parties you depend on.
- Internal Linux host posture (optional). A lightweight agent adds the inside view: missing patches, risky services, configuration drift and vulnerable application components.
- Threat intelligence that is about you. Notifications are matched to the technologies you actually run, not a generic news feed.
Interested in ReconX Attack Surface Management?
Tell us what you need - tick it in the contact form and our team will come back to you.
Contact us