The Pro CISO Newsletter
The security news our team thinks matters, about once a month · choose your topics · unsubscribe at any time
-
Threat Intel
Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups
GBHackers ·
Attackers abused compromised ConnectWise Cloud Backup credentials to access Microsoft 365 customer environments, prompting ConnectWise to shut off application access and interrupt...
-
Threat Intel
Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years
GBHackers ·
Anthropic says an internal Claude research model reconstructed how the National Security Agency generated seeds for five NIST elliptic curves in under 30 minutes, addressing a cryp...
-
Threat Intel
Critical WordPress Flaws Allow Attackers to Execute Remote Code Without Authentication
GBHackers ·
Two WordPress Core vulnerabilities can be chained to execute remote code without authentication, according to analysis by Seqrite researcher Amruta Wagh. Dubbed WP2Shell, the explo...
-
Threat Intel
OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root
GBHackers ·
A newly disclosed OpenBSD kernel exploitation chain combines a shared memory accounting flaw with a separate out-of-bounds write to obtain root privileges. Calif researcher Andrew...
-
Threat Intel
GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories
GBHackers ·
GhostAction attackers have expanded their GitHub credential theft campaign with a second stage that disguises malicious JavaScript as a font file and targets developer workstations...
-
Threat Intel
SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data
GBHackers ·
Indian authorities have warned that SideCopy hackers are targeting Indian organizations, including academic institutions, with spear-phishing attacks that deploy ReverseRAT on Wind...
-
Threat Intel
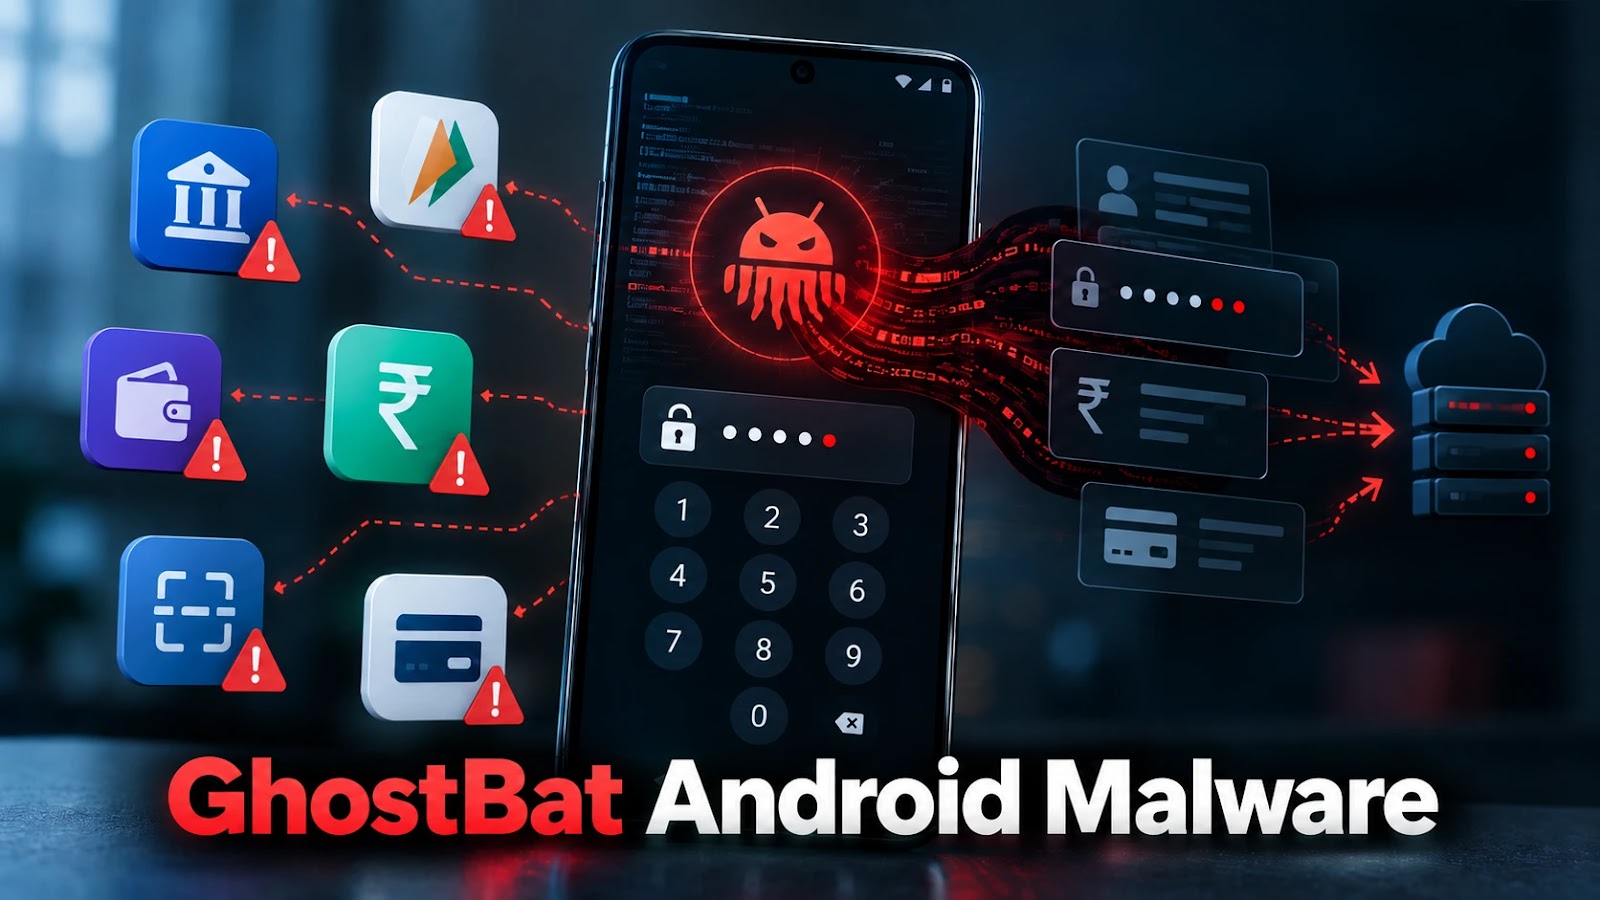
New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs
GBHackers ·
A new GhostBat RAT variant targets 60 Android financial application packages used in India, combining accessibility-based PIN capture with a transparent overlay that intercepts int...
-
Threat Intel
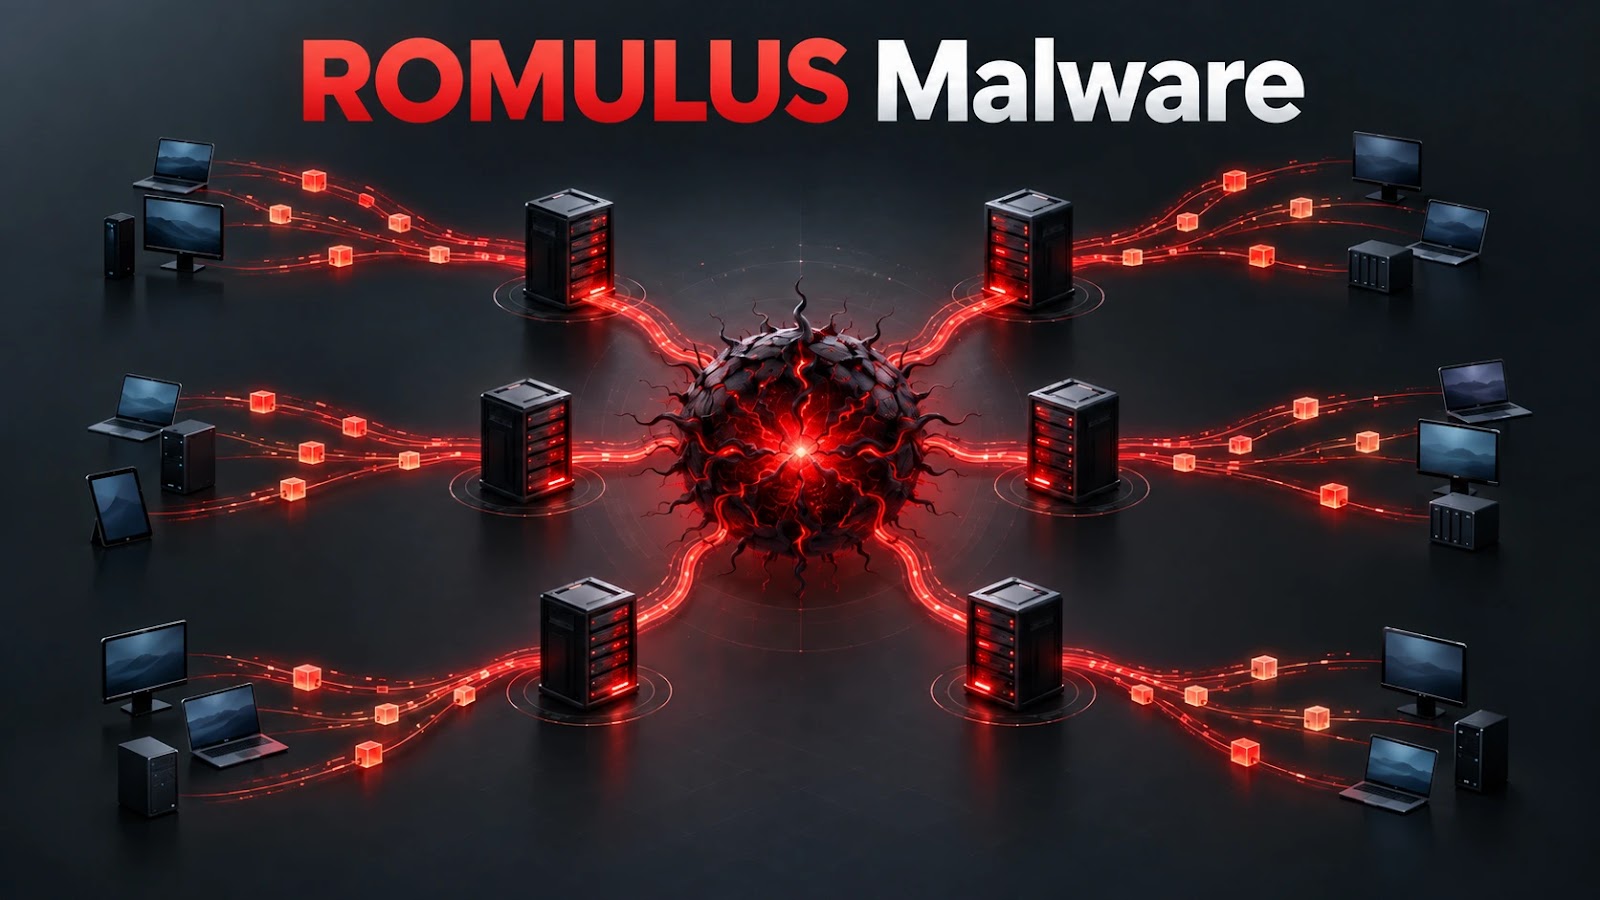
New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads
GBHackers ·
ROMULUS, a shared ClickFix delivery platform operating across six identified servers, with confirmed routes distributing a trojanized Stardock package and LegionLoader. The discove...
-
Threat Intel
Midnight Blizzard-Linked Malware Server Still Delivering Payloads 8 Weeks After Disclosure
GBHackers ·
A server linked to a malware campaign attributed to a Midnight Blizzard-associated cluster was still delivering malicious files on October 5, 2026. The server returned HTTP 200 res...
-
Threat Intel
Android Malware Exposes Its Own Operators While Hijacking Phones and Stealing Sensitive Data
GBHackers ·
An Android remote-access Trojan, YuanKong, whose weakly protected dropper reveals more than its hidden payload: it exposes the operator account identifiers embedded in each build....
-
Threat Intel
AI-Assisted Hackers Compromise Government Linux Servers to Deploy Backdoors and Steal Credentials
GBHackers ·
Hackers used AI-assisted scripts to compromise government Linux servers, harvest administrator credentials, and establish persistent backdoors during a campaign observed between Oc...
-
Threat Intel
Researchers Demonstrate iOS 27.0.1 Untethered Jailbreak on iPhone 18 Pro
GBHackers ·
Security researchers from Calif (Calif.io) demonstrated a working untethered jailbreak on iOS 27.0.1 running on an iPhone 18 Pro. They showed it live at the Hexacon 2026 offensive...
-
Threat Intel
Progress Warns of MOVEit Transfer Vulnerabilities Allowing Authentication Bypass and Privilege Escalation
GBHackers ·
Progress Software has released fixes for 12 vulnerabilities in MOVEit Transfer, its managed file transfer (MFT) platform. Several of the flaws allow authentication bypass, session...
-
Threat Intel
MITRE ATT&CK v20 Adds New AI Attack Techniques for Prompt Injection and Data Theft
GBHackers ·
MITRE released ATT&CK v20 on October 13, 2026. It adds the first Enterprise techniques for direct and indirect prompt injection, AI-enabled exfiltration and AI result poisoning. MI...
-
Threat Intel
Google Chrome 155 Patches Critical Use-After-Free Flaw and Nine Additional Security Bugs
GBHackers ·
Google has released Chrome 155 to the Stable channel with 10 security fixes. One is rated Critical: a use-after-free in Prerender, tracked as CVE-2026-110922. The update was publis...