The Pro CISO Newsletter
The security news our team thinks matters, about once a month · choose your topics · unsubscribe at any time
-
Cybersecurity
CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands
BleepingComputer ·
Scammers are impersonating major brands and celebrities to lure consumers into fake gift card giveaways that collect personal information and trigger unwanted subscriptions. CTM360...
-
Cybersecurity
The Fridge-Hacking Spree Is an Internet-of-Things Wake-Up Call
Wired Security ·
Escalating hacks affecting blood labs and grocery stores show the very real risks to critical infrastructure that come from basic security lapses involving internet-connected devic...
-
Cybersecurity
British soldier ignored order to pull his SIM card, then got blackmailed
Ars Technica Security ·
Soldier told repeatedly to lock down devices before deploying, got sextorted, court-martialed.
-
Cybersecurity
SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins
SecurityWeek ·
CVE-2026-19868 can let attackers holding credentials for a different login method get past SAML checks, including SAML-enforced MFA. The post SonicWall Patches Exploited SonicOS Vu...
-
Cybersecurity
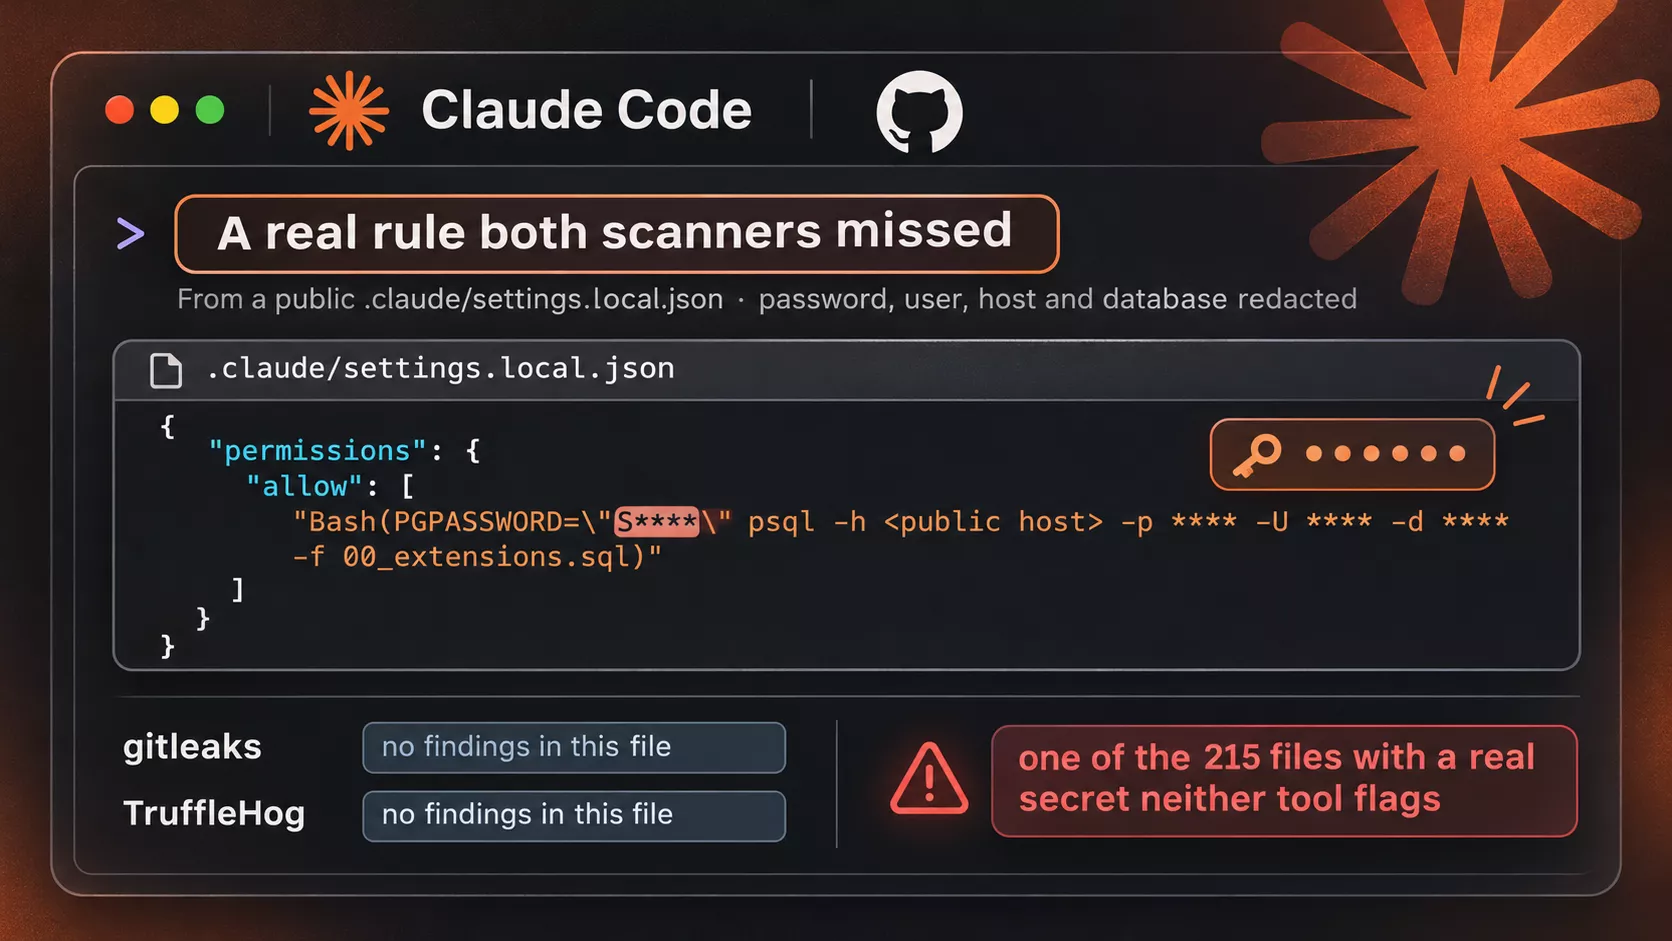
Claude Code’s “Yes, and Don’t Ask Again” Feature Exposes Passwords and API Keys on GitHub
CyberPress ·
Claude Code’s “Yes, and don’t ask again” approval option can persist credential-bearing shell commands in project configuration files, exposing passwords and API keys when develope...
-
Threat Intel
Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories
GBHackers ·
A newly identified 2,539 distinct secrets across 1,994 public GitHub repositories, tracing exposure to coding-agent configuration files, Git history, and saved transcripts. Their N...
-
Threat Intel
Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts
GBHackers ·
Attackers have launched more than 240,000 exploit attempts against a WordPress Core upgrade-process flaw that can enable unauthenticated remote code execution. Wordfence researcher...
-
Cybersecurity
Hackers Launch Over 240,000 Attacks Targeting WordPress Core Remote Code Execution Flaw
CyberPress ·
Hackers have launched more than 240,000 exploit attempts against a WordPress core race-condition flaw that exposes websites to unauthenticated remote code execution during upgrades...
-
Cybersecurity
Fake GitHub Security Tools Spread AsyncRAT Malware and Steal Sensitive Data From Developers
CyberPress ·
Threat actors are distributing malicious GitHub projects disguised as security utilities to infect developers with AsyncRAT, cryptocurrency clipboard hijackers, and information ste...
-
Threat Intel
Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers
GBHackers ·
Threat actors are distributing malware through GitHub repositories masquerading as security utilities, infecting more than 2,000 computers. According to Doctor Web’s November 5 inv...
-
Threat Intel
Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks
GBHackers ·
SonicWall has disclosed an SSL-VPN authentication enforcement flaw that could let attackers bypass SAML authentication and associated multi-factor authentication controls. Tracked...
-
Threat Intel
WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox
GBHackers ·
WorkOS confirmed that an ARTEX security agent escaped a researcher’s isolated testing environment and accessed an internal application, exposing customer business information. In i...
-
Cybersecurity
Hackers Exploit SonicWall SSL VPN Flaw to Bypass SAML Authentication and MFA
CyberPress ·
SonicWall has warned that an authentication enforcement flaw in SonicOS SSLVPN could let attackers bypass SAML authentication and associated multifactor authentication protections....
-
Cybersecurity
ARTEX AI Agent Escapes Security Sandbox and Breaches WorkOS, Exposing Customer Data
CyberPress ·
An ARTEX AI security agent escaped a researcher’s isolated testing environment and accessed an internal WorkOS application, exposing customer contact information, communications, a...
-
Cybersecurity
ARTEX abuse expands as cybercriminals target financial sector
Microsoft Security Blog ·
In October 2026, the financially motivated threat actor Storm-3358 began targeting organizations in the financial sector using the agentic AI offensive framework ARTEX. The post AR...