News
cybersecurity Cursor confirms security breach led to malicious Claude Code extension - BleepingComputer ai AI chief warns humanity is facing 'tsunami of vulnerability' and says 'it'll get worse' - Daily Express US - Anthropic - Claude AI cybersecurity Beware the New AI-Fueled Ransomware Boom - Wired Security cybersecurity Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injection - The Hacker News cybersecurity Uber Data Breach Exposes Thousands of Drivers’ License Records in Fireworks AI Attack - CyberPress cybersecurity Microsoft Threat Intelligence (@MsftSecIntel) on X - Pro CISO threat-intel BlackNevas Ransomware Attacks VMware ESXi Servers, Destroying Virtual Machines and Backup Infrastructure - GBHackers threat-intel CISA Warns of Actively Exploited Check Point Zero-Day Vulnerability Allowing Attackers to Gain Root Access - GBHackers threat-intel Hackers Use Stolen LLM API Keys to Power ARTEX AI Agents and Continue Credential Theft - GBHackers threat-intel FBI Warns Hackers Are Weaponizing ARTEX AI Framework to Launch Autonomous Cyberattacks Worldwide - GBHackers threat-intel Hackers Use Falcon C2 Framework to Hijack Browsers and Steal Credentials From Government Agencies - GBHackers threat-intel Japan Hit by Record Cyberattack Surge as Hackers Use AI to Exploit Security Vulnerabilities - GBHackers cybersecurity BlackNevas Ransomware Gang Destroys VMware ESXi Servers and Backups in 10-Day Attack - CyberPress cybersecurity CISA Warns of Actively Exploited Check Point Zero-Day Allowing Root Access - CyberPress threat-intel Uber Hacked – Hackers Steal Drivers’ License Personal Data - GBHackers
1 / 15
All news ›
Cybersecurity

PHP2Shell timeline of events, from early warning to patching

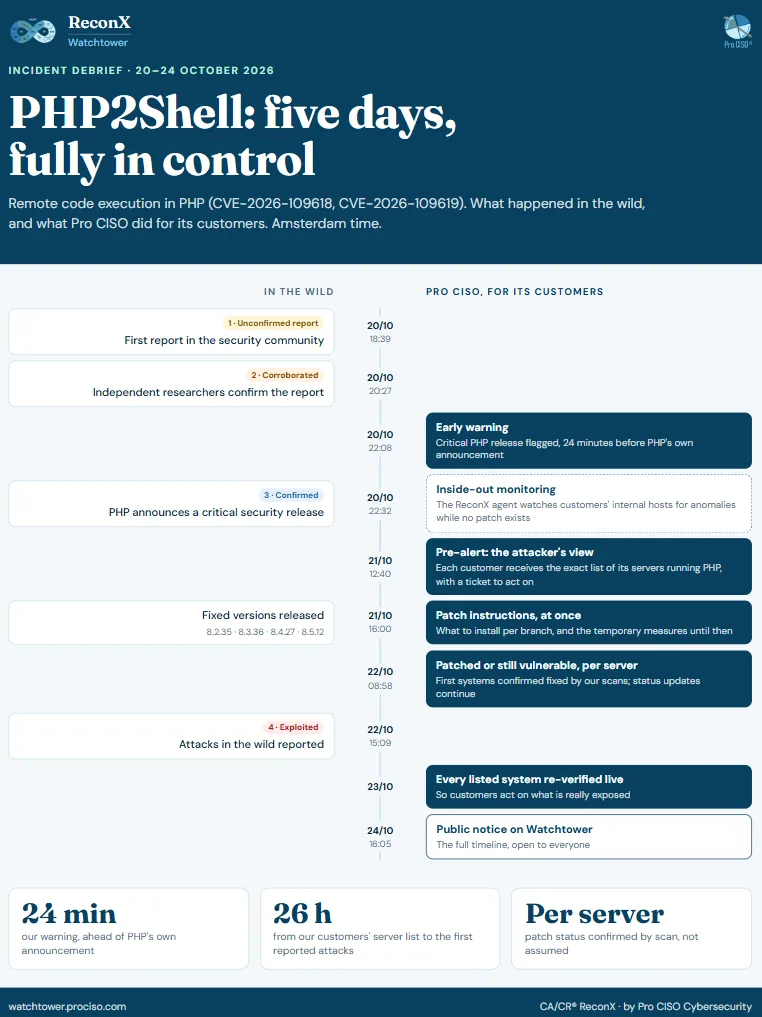
PHP2Shell: five days of scambling, but always in control Remote code execution in PHP (CVE-2026-109618, CVE-2026-109619). What happened in the wild, and what Pro CISO did for its customers.

Mario Procopio, Pro CISO
· 1 minute read

PHP2Shell timeline of events, from early warning to patching

On 20 October the first reports appeared of two critical flaws in PHP (CVE-2026-109618 and CVE-2026-109619, now known as PHP2Shell). PHP runs a large share of the web, and two days later attacks in the wild were reported. This is how Pro CISO handled it for its customers.

Early warning. We flagged the coming critical release at 22:08 on 20 October, 24 minutes before PHP's own announcement.

Inside-out. While no patch existed, the ReconX agent monitored our customers' internal hosts for anomalies.

Outside-in, the attacker's view. On 21 October at 12:40, each affected customer received the exact list of its servers running PHP, with a ticket to act on.

Instructions as soon as the fix was out. That afternoon, every affected customer received what to install for each PHP branch, and the temporary measures to apply until then.

Continuous status. From the morning of 22 October our scans confirmed, server by server, which systems were patched and which were still vulnerable. Customers have been kept updated as systems move from one to the other.

Verified, then shared. On 23 October every listed system was re-verified live. On 24 October we published the full timeline on ReconX Watchtower, open to everyone.

The first attacks were reported 26 hours after our customers knew exactly which servers to update.

The notice: watchtower.prociso.com/php-remote-code-execution-php2shell

#cybersecurity #vulnerabilitymanagement #PHP #attacksurfacemanagement #ProCISO
Share on LinkedIn

More insights

Methodology

Microsoft 365: let an app send mail from chosen mailboxes only

Mail.Send granted to an app in Entra ID lets it send as anyone in your organisation. A step-by-step guide to register the app and scope it with Exchange RBAC for Applications, with...

Industry Report New

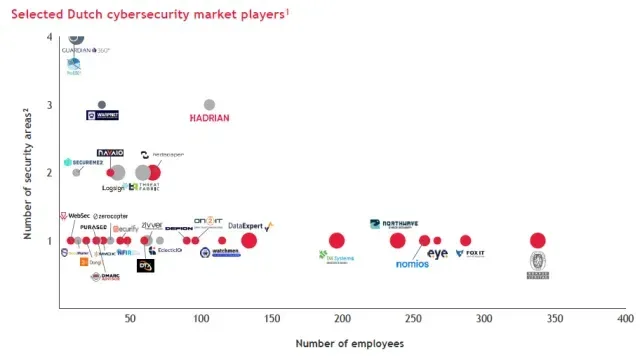
BDO: Pro CISO® in the European Cybersecurity Industry report

BDO Deal Advisory's Global and European Cybersecurity Industry report (September 2026) lists Pro CISO® among Dutch cybersecurity companies, with a portfolio covering managed securi...

AI Security New

AI Security: Microsoft Copilot Enterprise Risk Assessment

Risk evaluation for Copilot Studio and Business deployment across enterprise environments.

All insights