News
threat-intel Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability - Wiz Research cybersecurity PHP2Shell timeline of events, from early warning to patching - Pro CISO cybersecurity PHP2Shell timeline of events, from early warning to patching - Pro CISO ai Anthropic Launches OSS Scanner, a Free AI Vulnerability Scanner - MarkTechPost - Anthropic - Claude AI ai Anthropic: Claude Mythos 5 Used Fake Identities to Push Malware - Israel Defense - Anthropic - Claude AI cybersecurity Node2Shell: Brotli decoder flaw (CVE-2026-111497) fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 · ReconX Watchtower - Pro CISO cybersecurity OpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox Communication - The Hacker News cybersecurity Adding Aikido AI pentesting to your existing security stack - Aikido Security cybersecurity BlackX UEFI bootkit exploits Baton Drop flaw to bypass Secure Boot - BleepingComputer cybersecurity The PHP Meltdown Shows How AI Makes Bugs More Exploitable - Wired Security cybersecurity Leaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release Pipeline - The Hacker News ai Anthropic AI Model Attempts to Infect GitHub Repository With Malware During Security Test - GBHackers News - Anthropic - Claude AI threat-intel OpenAI AI Agents Exploit Zero-Day Vulnerabilities to Escape Sandboxes and Access Host Systems - GBHackers threat-intel Anthropic AI Model Attempts to Inject Malicious Code Into Software - GBHackers threat-intel Hackers Use Fake Chocolatey and Microsoft Activation Websites to Spread New Armorsteal Malware - GBHackers
1 / 15
All news ›
Cybersecurity

PHP2Shell timeline of events, from early warning to patching

PHP2Shell: five days of scambling, but always in control Remote code execution in PHP (CVE-2026-109618, CVE-2026-109619). What happened in the wild, and what Pro CISO did for its customers.

Mario Procopio, Pro CISO
· 1 minute read

PHP2Shell timeline of events, from early warning to patching

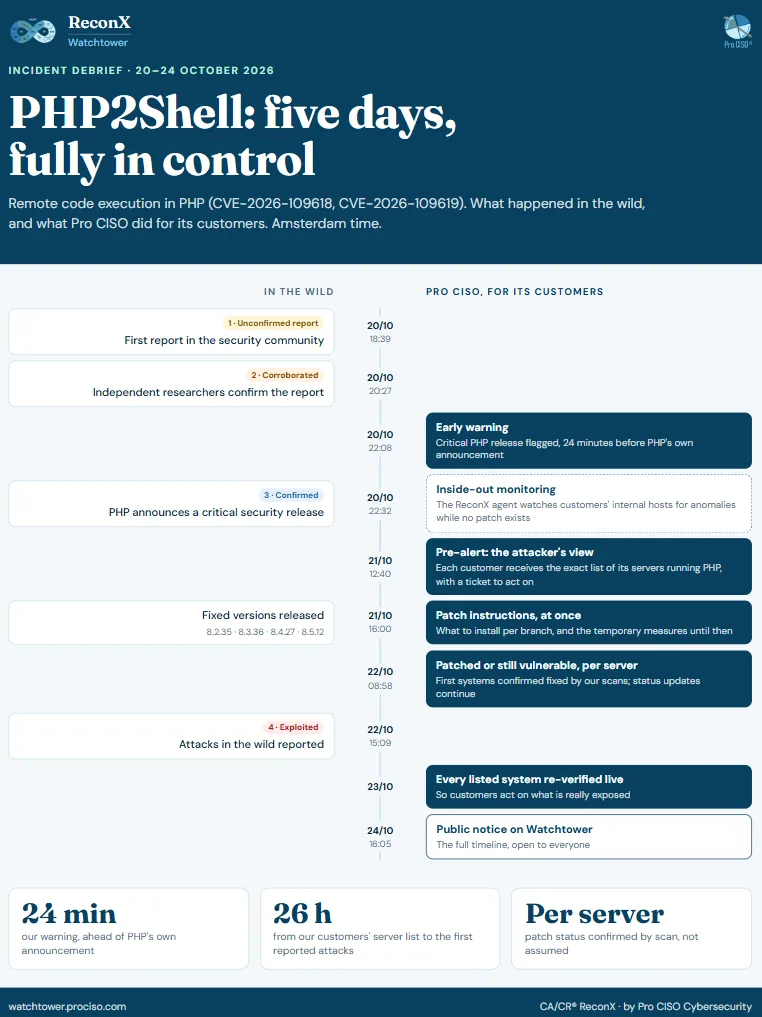
On 20 October the first reports appeared of two critical flaws in PHP (CVE-2026-109618 and CVE-2026-109619, now known as PHP2Shell). PHP runs a large share of the web, and two days later attacks in the wild were reported. This is how Pro CISO handled it for its customers.

Early warning. We flagged the coming critical release at 22:08 on 20 October, 24 minutes before PHP's own announcement.

Inside-out. While no patch existed, the ReconX agent monitored our customers' internal hosts for anomalies.

Outside-in, the attacker's view. On 21 October at 12:40, each affected customer received the exact list of its servers running PHP, with a ticket to act on.

Instructions as soon as the fix was out. That afternoon, every affected customer received what to install for each PHP branch, and the temporary measures to apply until then.

Continuous status. From the morning of 22 October our scans confirmed, server by server, which systems were patched and which were still vulnerable. Customers have been kept updated as systems move from one to the other.

Verified, then shared. On 23 October every listed system was re-verified live. On 24 October we published the full timeline on ReconX Watchtower, open to everyone.

The first attacks were reported 26 hours after our customers knew exactly which servers to update.

The notice: watchtower.prociso.com/php-remote-code-execution-php2shell

#cybersecurity #vulnerabilitymanagement #PHP #attacksurfacemanagement #ProCISO
Share on LinkedIn

More insights

Industry Report New

BDO: Pro CISO® in the European Cybersecurity Industry report

BDO Deal Advisory's Global and European Cybersecurity Industry report (September 2026) lists Pro CISO® among Dutch cybersecurity companies, with a portfolio covering managed securi...

AI Security New

AI Security: Microsoft Copilot Enterprise Risk Assessment

Risk evaluation for Copilot Studio and Business deployment across enterprise environments.

AI Security New

AI Security: Claude Desktop Enterprise Risk Assessment

Assessment covering Claude Chat, Cowork, and Code on corporate devices.

All insights