News
threat-intel Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network - GBHackers cybersecurity Malicious cPGuard Updates Served in OpsShield Supply Chain Attack - SecurityWeek cybersecurity Cloudflare Introduces Zero Wire to Help Security Teams Track Critical CVEs and Exploits - CyberPress cybersecurity Rigged Coding Assignment, Abused AI Tool Opened Path to $6 Billion Binance Heist - SecurityWeek threat-intel Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware - GBHackers cybersecurity Hackers use n-day exploits in zero-click attacks on iOS, Android devices - BleepingComputer cybersecurity Hackers Use AI-Driven Ransomware Attack to Encrypt 37 Systems Across UK Schools - CyberPress threat-intel Hackers Use Stolen Credentials to Fake Major Data Breaches and Pressure Companies for Money - GBHackers cybersecurity Hackers Hijack Cloud AI Models in LLMJacking Attacks, Leaving Victims With $1 Million Bills - CyberPress threat-intel mSecure Password Manager Reports Suspicious Activity, Urges Users to Change All Stored Passwords - GBHackers threat-intel Google Warns of LLMJacking Attacks That Generate Over $100,000 in Cloud AI Bills Per Day - GBHackers threat-intel Hackers Are Stealing ChatGPT and Claude Tokens That Changing Your Password May Not Stop - GBHackers cybersecurity Russian Police Arrest 3 Suspected VasyGrek Hackers, Dismantle Criminal Infrastructure - The Hacker News threat-intel Microsoft Edge Now Automatically Blocks Malicious Browser Notifications Used in Scareware Attacks - GBHackers cybersecurity Fake Microsoft Support Scam Reaches Users at 80 Organizations Through Malicious Online Ads - CyberPress
1 / 15
All news ›
Threat Intel

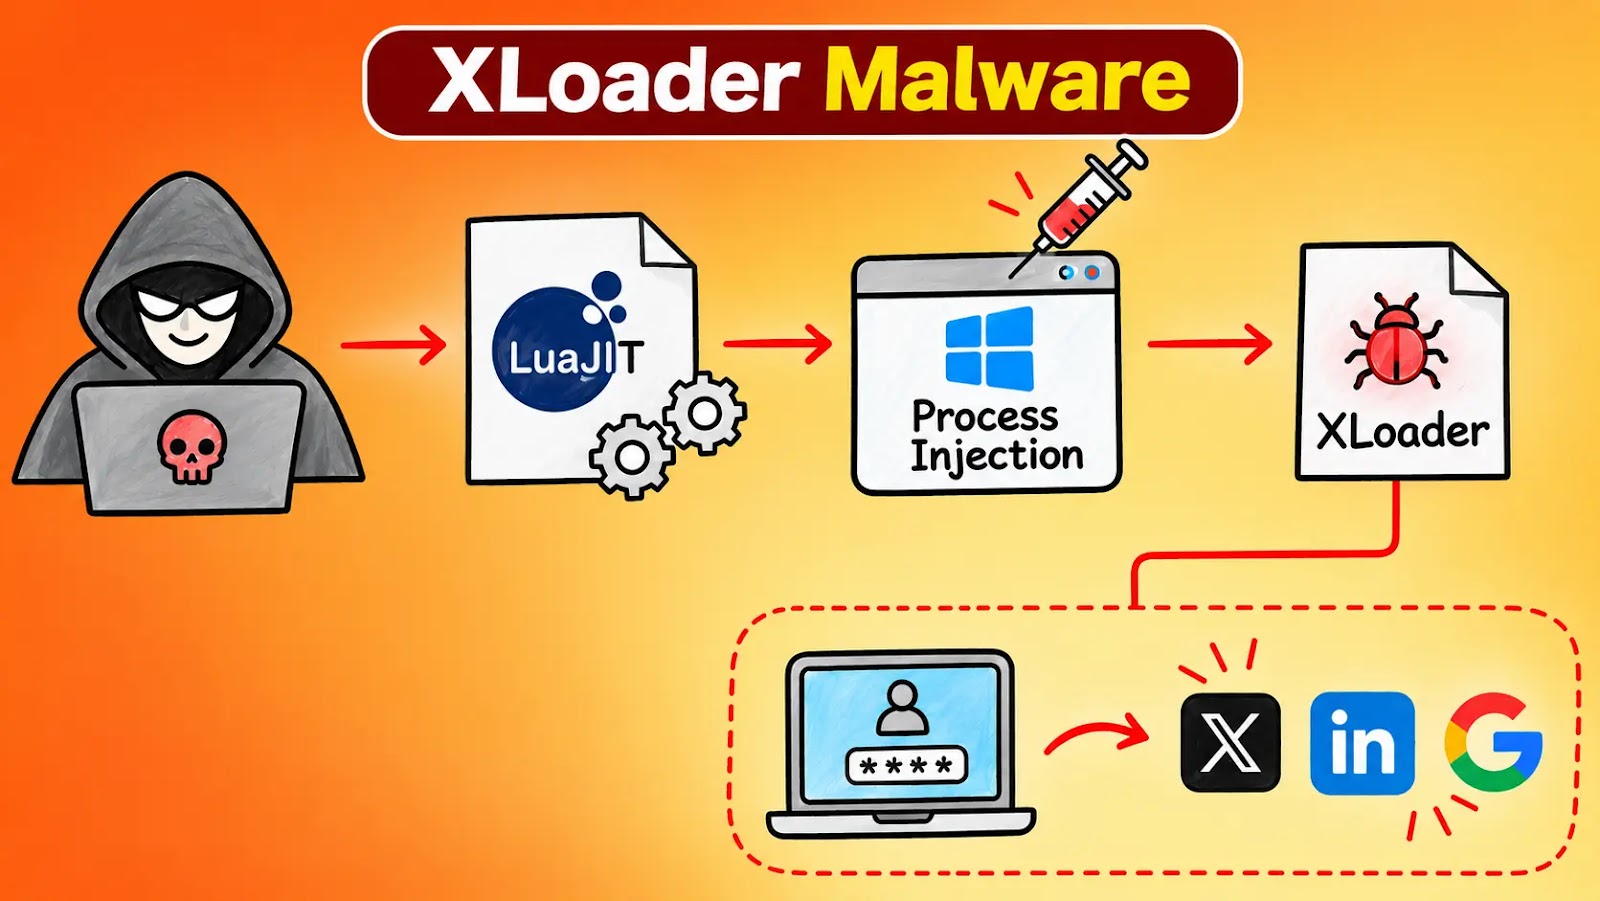
Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware

A new XLoader infection chain. It hides the credential stealer inside an embedded LuaJIT interpreter. It moves it into another Windows process through shared-section injection. The campaign uses business-themed email lures. It also delivered Agent Tesla, Remcos and XWorm . The chain starts with order and payment emails. One Greek-language message has a subject starting […] The post Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform .

Continue on GBHackers ↗ ‹ All news Get the newsletter

The summary and image come from GBHackers; the image is shown from their website.