News
cybersecurity CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands - BleepingComputer cybersecurity The Fridge-Hacking Spree Is an Internet-of-Things Wake-Up Call - Wired Security cybersecurity British soldier ignored order to pull his SIM card, then got blackmailed - Ars Technica Security cybersecurity SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins - SecurityWeek cybersecurity Claude Code’s “Yes, and Don’t Ask Again” Feature Exposes Passwords and API Keys on GitHub - CyberPress threat-intel Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories - GBHackers threat-intel Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts - GBHackers cybersecurity Hackers Launch Over 240,000 Attacks Targeting WordPress Core Remote Code Execution Flaw - CyberPress cybersecurity Fake GitHub Security Tools Spread AsyncRAT Malware and Steal Sensitive Data From Developers - CyberPress threat-intel Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers - GBHackers threat-intel Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks - GBHackers threat-intel WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox - GBHackers cybersecurity Hackers Exploit SonicWall SSL VPN Flaw to Bypass SAML Authentication and MFA - CyberPress cybersecurity ARTEX AI Agent Escapes Security Sandbox and Breaches WorkOS, Exposing Customer Data - CyberPress cybersecurity ARTEX abuse expands as cybercriminals target financial sector - Microsoft Security Blog
1 / 15
All news ›
Threat Intel

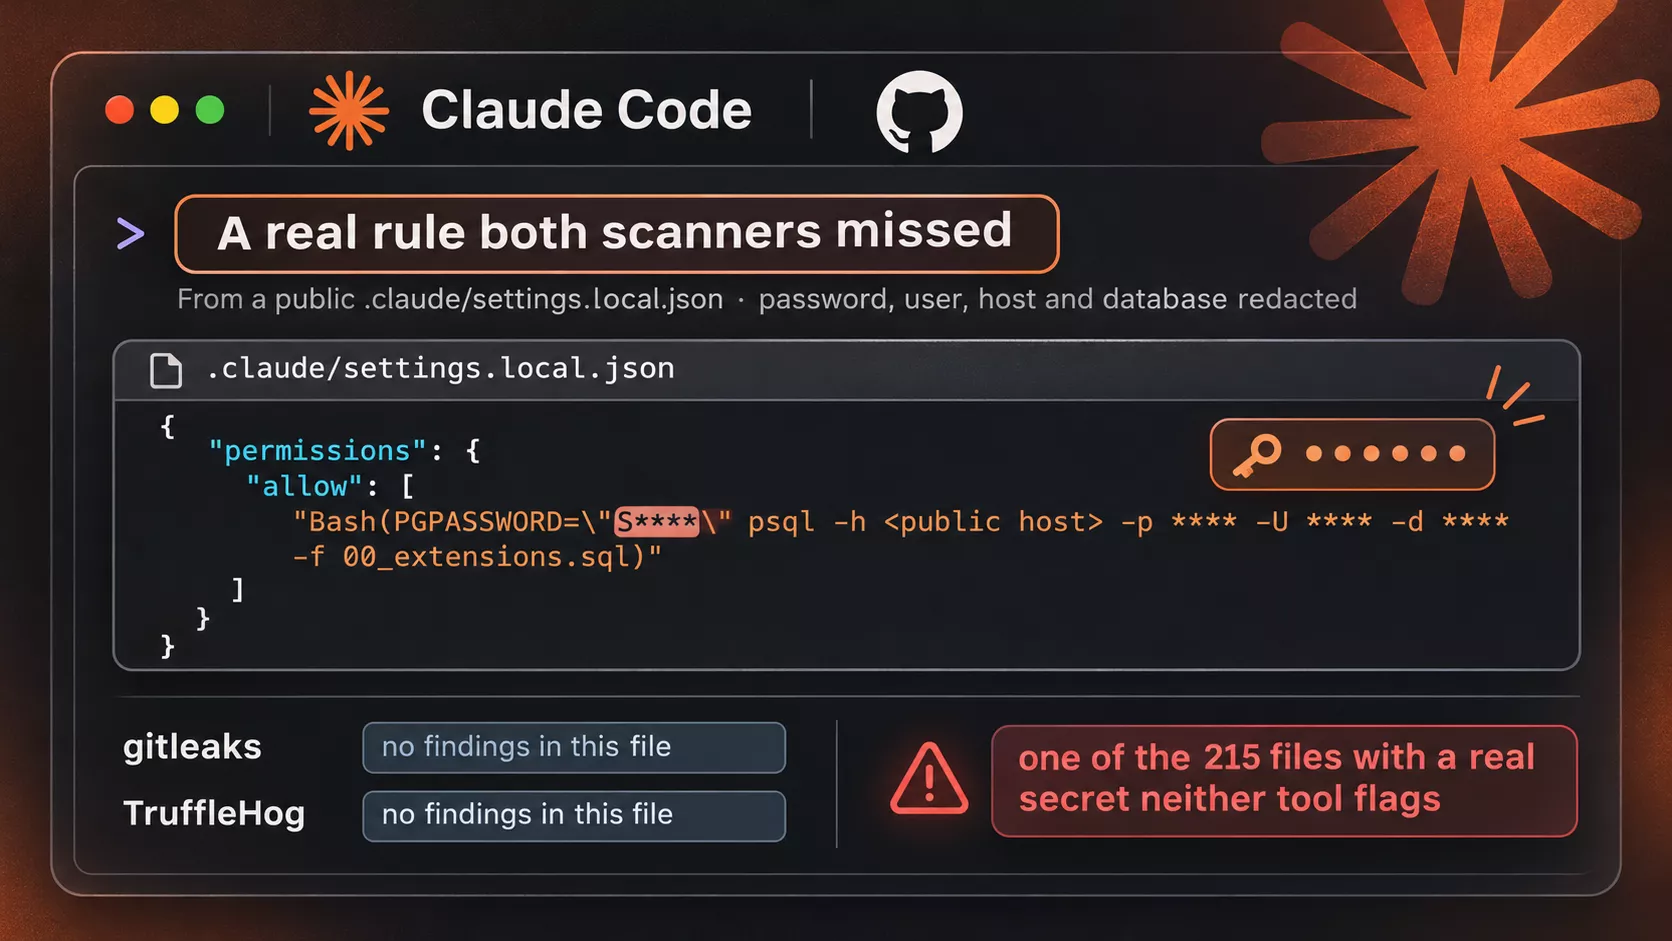
Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories

A newly identified 2,539 distinct secrets across 1,994 public GitHub repositories, tracing exposure to coding-agent configuration files, Git history, and saved transcripts. Their November 5 research describes how Claude Code’s “Yes, and don’t ask again” approval can persist credential-bearing shell commands inside .claude/settings.local.json. Exposed material included production database passwords, cloud credentials, API tokens, and SSH […] The post Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform .

Continue on GBHackers ↗ ‹ All news Get the newsletter

The summary and image come from GBHackers; the image is shown from their website.