News
cybersecurity Scans for Sshole Vulnerability (CVE-2026-123158), (Sun, Nov 8th) - SANS Internet Storm Center cybersecurity Hackers pull off $133 million French bank heist via service provider - BleepingComputer cybersecurity CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands - BleepingComputer cybersecurity The Fridge-Hacking Spree Is an Internet-of-Things Wake-Up Call - Wired Security cybersecurity British soldier ignored order to pull his SIM card, then got blackmailed - Ars Technica Security cybersecurity SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins - SecurityWeek cybersecurity Claude Code’s “Yes, and Don’t Ask Again” Feature Exposes Passwords and API Keys on GitHub - CyberPress threat-intel Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories - GBHackers threat-intel Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts - GBHackers cybersecurity Hackers Launch Over 240,000 Attacks Targeting WordPress Core Remote Code Execution Flaw - CyberPress cybersecurity Fake GitHub Security Tools Spread AsyncRAT Malware and Steal Sensitive Data From Developers - CyberPress threat-intel Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers - GBHackers threat-intel Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks - GBHackers threat-intel WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox - GBHackers cybersecurity Hackers Exploit SonicWall SSL VPN Flaw to Bypass SAML Authentication and MFA - CyberPress
1 / 15
All news ›
Cybersecurity

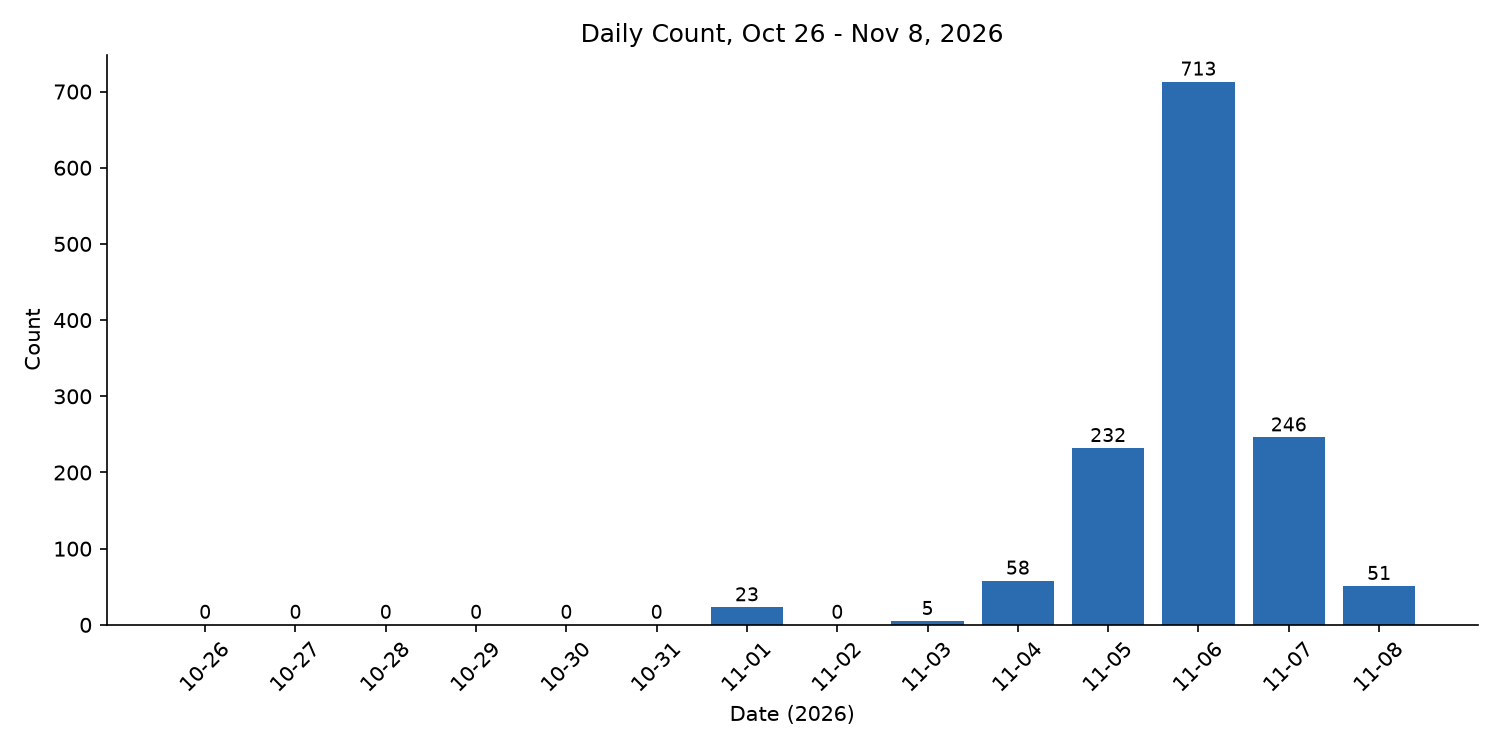
Scans for Sshole Vulnerability (CVE-2026-123158), (Sun, Nov 8th)

Our honeypots use "Cowrie" to collect SSH data. With the emergence of the "sshole" vulnerability last week, we are now seeing an increase in attempts to exploit the vulnerability. Our data is a bit limited in this respect. Our honeypots collect only the first 255 characters of SSH passwords. Longer passwords are highly unusual and not used for the usual password brute-forcing we observe.

Continue on SANS Internet Storm Center ↗ ‹ All news Get the newsletter

The summary and image come from SANS Internet Storm Center; the image is shown from their website.